Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Assured Workloads for Regulated Data Residency
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
A multinational financial services enterprise is expanding its operations across both the United States and the European Union. The enterprise must deploy multiple cloud-based application environments that comply with strict regulatory frameworks, including US government compliance regimes (such as FedRAMP/CJIS) and EU data sovereignty regulations.
The enterprise has the following technical and compliance requirements:
- Workload environments must automatically enforce data residency to geographically compliant cloud regions.
- Technical support cases and personnel access to operational telemetry must be restricted to qualified personnel within the respective geographic jurisdictions.
- Automated organizational policy constraints must prevent administrators from provisioning resources outside compliant boundaries.
Which solution should you implement to satisfy these compliance and governance requirements?
Explanations
Implement Cloud Data Loss Prevention (Sensitive Data Protection) inspection templates to scan and relocate non-compliant data across standard folders.
Implement Cloud Data Loss Prevention (Sensitive Data Protection) inspection templates to scan and relocate non-compliant data across standard folders.
What Cloud DLP is
Cloud Data Loss Prevention (now part of Sensitive Data Protection) provides automated discovery, classification, and de-identification of sensitive data elements (such as PII, credit card numbers, and health records) within structured and unstructured datasets.
Why it doesn't meet the requirement
- Preventative Infrastructure Controls: Cloud DLP is a data inspection and transformation tool; it does not enforce infrastructure-level deployment boundaries or restrict where compute/storage infrastructure can be provisioned.
- Personnel Access and Governance: Cloud DLP has no role in restricting Google technical support routing, managing administrative support access by geography, or enforcing project-level organizational policies.
Key characteristics and limitations
- Scans data at rest and data in transit for sensitive infoTypes.
- De-identifies data using masking, tokenization, and bucketing.
- Does not enforce operational or regional boundary guardrails on cloud infrastructure resources.
This answer would be correct if
The core objective was to discover, classify, and redact sensitive personal identifiers (PII) embedded inside application payloads and database fields prior to analytics processing.
Create Assured Workloads environments for the required US and EU compliance regimes, and deploy projects within their respective regulatory folders.
Create Assured Workloads environments for the required US and EU compliance regimes, and deploy projects within their respective regulatory folders.
What Assured Workloads is
Assured Workloads is a Google Cloud solution that enables enterprise customers to easily configure, deploy, and enforce security and compliance boundaries for regulated workloads without managing custom policy orchestration independently.
How it meets the requirements
- Enforcing Data Residency: Assured Workloads enforces pre-configured Organization Policy constraints (such as resource location restrictions) at the folder level, ensuring that storage, compute, and data analytics resources can only be deployed in designated geographic regions (e.g., specific US or EU regions).
- Personnel Access Restrictions: Assured Workloads enforces sovereign and personnel controls that ensure technical support, access approvals, and platform maintenance requests are handled exclusively by verified personnel in the appropriate geographic jurisdiction (e.g., EU persons in EU locations for Sovereign Controls).
- Automated Guardrails: When an Assured Workloads folder is created, it automatically applies compliance-specific organizational constraints across all nested projects to prevent configuration drift and block non-compliant resource provisioning.
Assured Workloads Folder Guardrails (US & EU)
System Architecture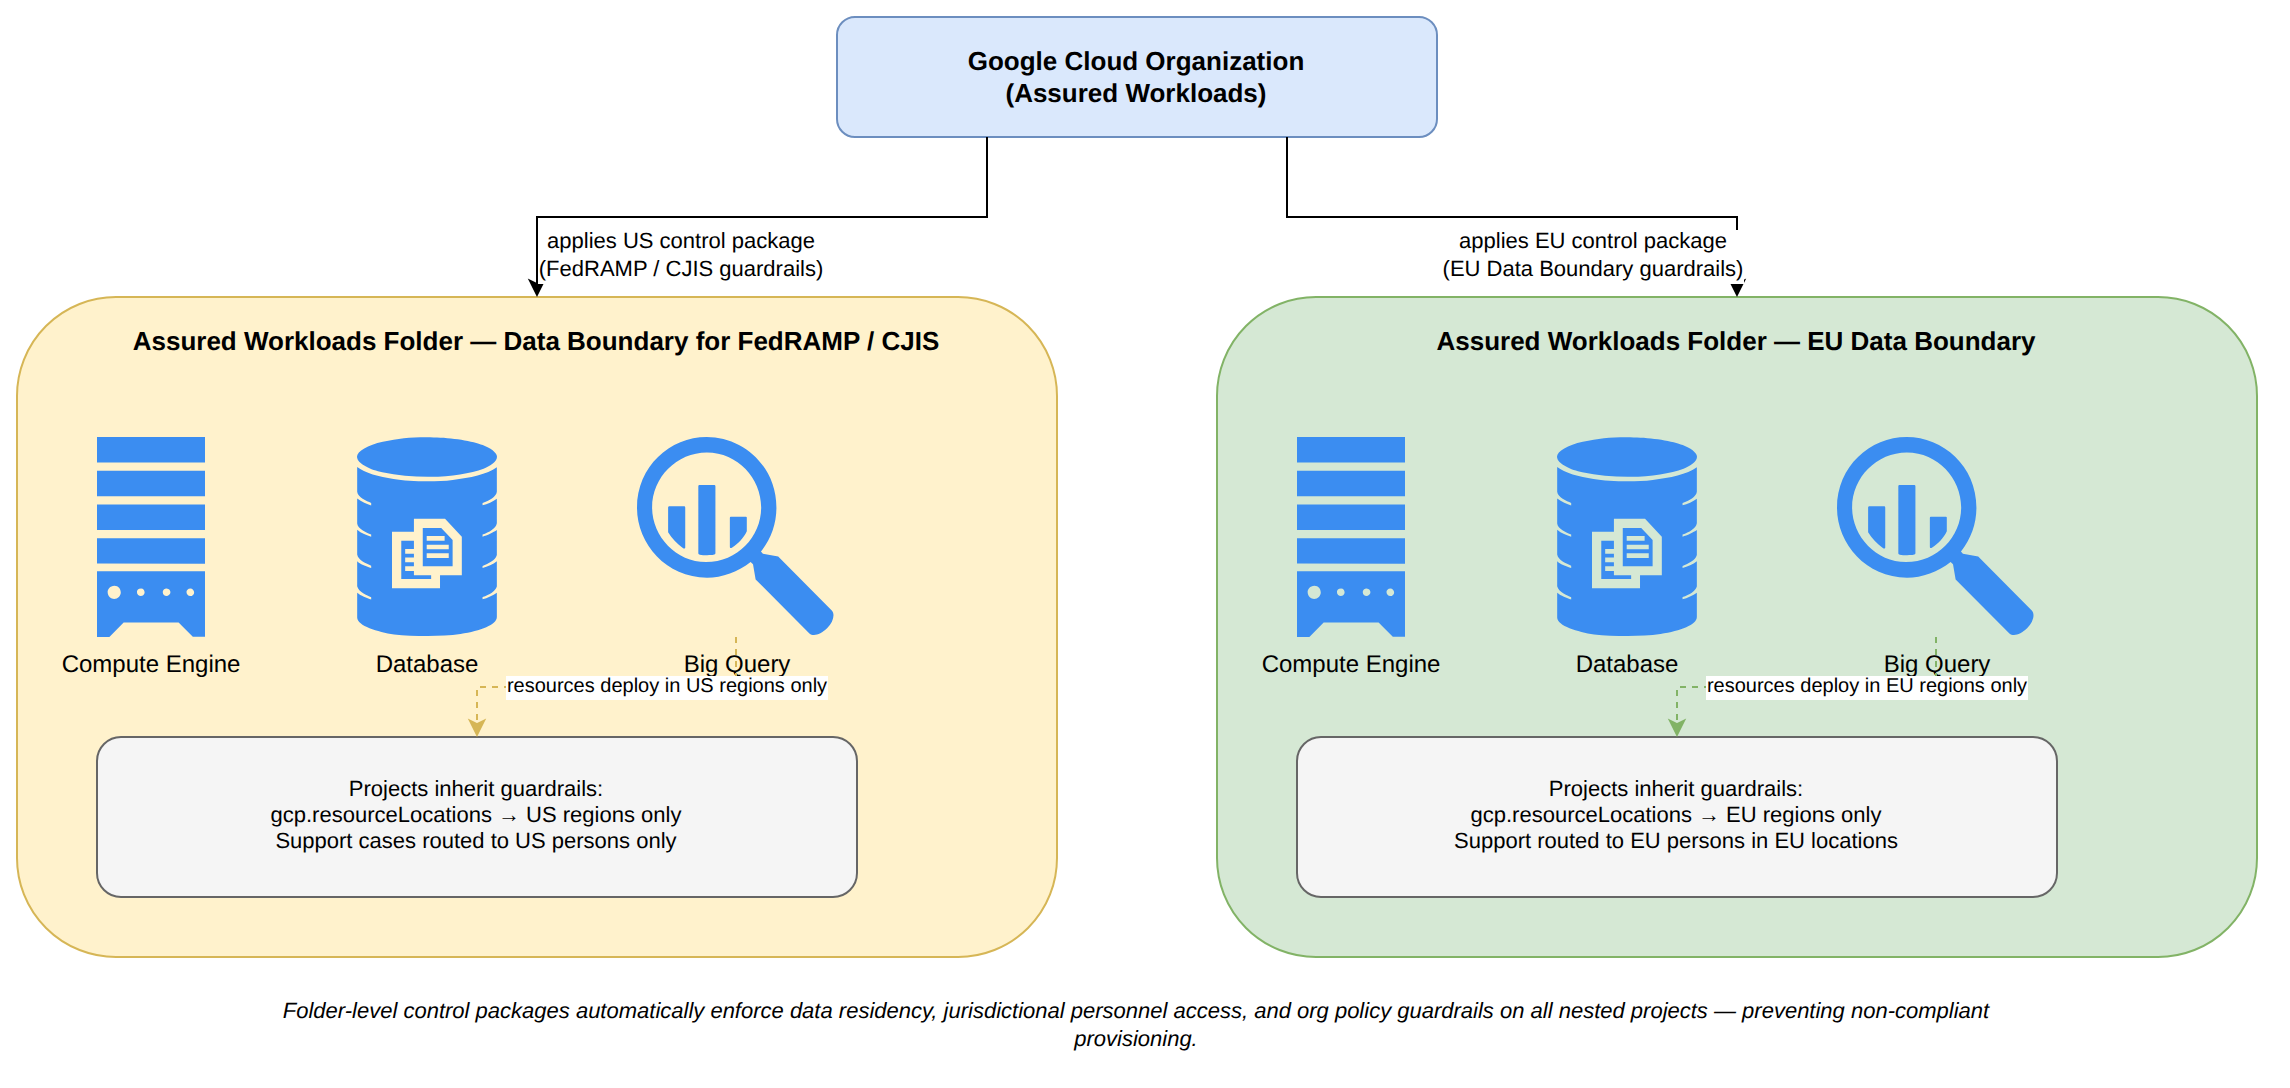
Key advantages and capabilities
- Pre-configured Compliance Regimes: Out-of-the-box support for FedRAMP, CJIS, IL4, EU Regions, and Sovereign Controls.
- Continuous Compliance Monitoring: Built-in compliance monitoring alerts administrators if policies or resources deviate from the required regulatory baseline.
- Integrated Encryption Controls: Works seamlessly with Cloud KMS and customer-managed encryption keys (CMEK) to meet regulatory encryption standards.
Why this is optimal
Using Assured Workloads provides platform-enforced compliance baselines backed by contractual and technical guarantees for data residency and support personnel jurisdiction. Implementing this natively avoids fragile custom scripting and manual auditing.
Create Cloud Key Management Service (Cloud KMS) Customer-Managed Encryption Keys (CMEK) and apply IAM roles across custom Resource Manager folders.
Create Cloud Key Management Service (Cloud KMS) Customer-Managed Encryption Keys (CMEK) and apply IAM roles across custom Resource Manager folders.
What Cloud KMS and IAM do
Cloud Key Management Service (Cloud KMS) enables cryptographic key lifecycle management, while Identity and Access Management (IAM) enforces role-based access control (RBAC) to govern identity permissions across resources.
Why it doesn't meet the requirement
- Comprehensive Compliance Regimes: While encryption key management and IAM are critical security components, configuring them manually does not establish formal compliance boundaries for regimes like FedRAMP or EU Sovereign Controls.
- Support Personnel Routing: Cloud KMS and standard IAM roles cannot enforce geographic routing constraints for Google Cloud technical support engineers or access approval transparency.
Key characteristics and limitations
- Provides cryptographic control of data at rest through customer-managed or external keys.
- Governs identity authorization based on the principle of least privilege.
- Lacks out-of-the-box automation for regulatory boundary validation and regional sovereign restrictions.
This answer would be correct if
The enterprise already had an established regulatory boundary and only needed to fulfill a cryptographic mandate to maintain control over encryption keys used by storage services.
Deploy standard Google Cloud projects and configure VPC Service Controls perimeters around all storage and compute resources in each region.
Deploy standard Google Cloud projects and configure VPC Service Controls perimeters around all storage and compute resources in each region.
What VPC Service Controls is
VPC Service Controls is a network security capability that allows organizations to define fine-grained perimeters around Google Cloud managed services (such as Cloud Storage and BigQuery) to prevent data exfiltration and restrict ingress/egress access.
Why it doesn't meet the requirement
- Personnel Support Restrictions: While VPC Service Controls creates a perimeter against unauthorized API access and network-level exfiltration, it does not manage or enforce Google support personnel access restrictions or geographical support routing.
- Compliance Regime Automation: VPC Service Controls does not automatically apply regulatory baselines (such as FedRAMP, CJIS, or EU Sovereign controls) across resource creation hierarchies.
Key characteristics and limitations
- Operates at the network and API level to isolate services.
- Mitigates insider threats and unauthorized data movement across organizational perimeters.
- Does not automatically enforce region-specific organizational policy baselines across broad compliance frameworks.
This answer would be correct if
The primary goal was strictly to prevent authorized identities from copying data from internal corporate storage buckets to external, untrusted projects on the public network.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Cloud FinOps
Business use cases and product strategy
IntermediateProfessional Cloud Architect
Cloud Spanner Active-Active Multi-Region
Business use cases and product strategy
IntermediateProfessional Cloud Architect
Monolith to Microservices on GKE with HPA
Cloud and technology improvements
IntermediateProfessional Cloud Architect
Application Integration
Identifying functional and non-functional requirements
IntermediateProfessional Cloud Architect
Cloud KMS Dedicated Key Project Architecture
Data security (key management, encryption, secret management)
AdvancedProfessional Cloud Security Engineer
Workload Identity Federation Attribute Mapping and Conditions
Configuring Workload Identity Federation.
Last updated