Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Hardware-Backed Client-Side Encryption for Workspace
Free sample question with answers and detailed explanation below. The Cloud Digital Leader practice bank has an additional 3,070 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
A healthcare organization uses Google Workspace to foster real-time communication and collaboration across its clinical and administrative teams. Because employees frequently share sensitive patient records and financial information via files and emails, the organization needs to strengthen its digital operations with additional security and compliance controls.
Specifically, the organization must meet the following requirements:
- Add a layer of client-side encryption (CSE) on top of the default encryption provided for files and emails.
- Store and manage hardware-backed encryption keys within FIPS 140-2 Level 3 compliant modules so key material never leaves the protection boundary.
- Ensure that protected collaboration data can only be encrypted and decrypted by users authorized through the organization's identity provider (IdP) to maintain HIPAA compliance.
Which Google Cloud solution should the organization implement?
Explanations
Confidential Computing
Confidential Computing
What Confidential Computing is and does
Confidential Computing is a Google Cloud security technology that encrypts data in use while it is being processed in system memory. It provides a hardware-based trusted execution environment (TEE) for compute workloads—including Confidential VM, Confidential Google Kubernetes Engine (GKE) Nodes, Confidential Dataflow, and Confidential Space—to protect sensitive applications and data in RAM from unauthorized access.
Why it doesn't meet the requirement
- Does not provide Google Workspace client-side encryption: Confidential Computing protects data inside system memory during compute processing on virtual machines and containers, rather than providing client-side encryption (CSE) for end-user emails and files in Google Workspace.
- Does not manage IdP-based file and email encryption keys: It is designed for infrastructure and analytics workloads rather than managing FIPS 140-2 Level 3 HSM keys tied to an identity provider (IdP) for Google Workspace collaboration.
Key characteristics and limitations
- Memory-level protection: Addresses the security gap where data is encrypted at rest and in transit by default, but would otherwise remain unencrypted while actively in use in system memory.
- Workload-specific scope: Applies to compute, container, and big data processing services such as Compute Engine, GKE, Dataflow, and Dataproc (Apache Spark).
- Trust boundary reduction: Reduces the organizational trust boundary by isolating memory contents from the underlying hypervisor and host operating system.
This answer would be correct if
This option would be the right choice if the organization were running custom healthcare analytics applications on Compute Engine VMs or GKE containers and needed to ensure that sensitive patient data remained encrypted while actively being processed in system memory.
Additional context
A complete cloud data protection strategy considers three states of data: at rest, in transit, and in use. While Confidential Computing secures data in use on cloud compute infrastructure, Cloud HSM for Google Workspace secures collaborative content at the client layer before it reaches Google's servers.
Google Workspace Alert Center
Google Workspace Alert Center
What Google Workspace Alert Center is and does
Google Workspace Alert Center is a centralized administrative monitoring and notification tool within Google Workspace that provides security alerts, actionable insights, and recommendations. It helps administrators detect, investigate, and respond to suspicious activities—such as potential account compromises, phishing attempts, or unauthorized changes to single sign-on (SSO) and two-step verification settings.
Why it doesn't meet the requirement
- Reactive monitoring rather than cryptographic encryption: Google Workspace Alert Center notifies administrators about potential security threats and policy anomalies, whereas the scenario requires proactive client-side encryption (CSE) for files and emails.
- Does not manage hardware-backed keys: It does not provide FIPS 140-2 Level 3 hardware security modules (HSMs) or perform cryptographic wrap and unwrap operations.
Key characteristics and limitations
- Centralized threat visibility: Consolidates alerts regarding suspicious login attempts, government-backed attacks, and leaked passwords affecting Google Workspace accounts.
- Integration with Security Command Center: Works alongside organization-level activations of Security Command Center and Event Threat Detection to surface log-based threat findings.
- Administrative remediation guidance: Helps administrators take corrective actions—such as resetting compromised passwords or enforcing 2-Step Verification—to restore account security.
This answer would be correct if
This option would be the right choice if a Google Workspace administrator needed a unified console to view real-time notifications, investigate suspicious login behavior, and follow recommended steps to remediate compromised user accounts.
Additional context
While Google Workspace Alert Center and Google Workspace Security Center play a vital role in operational threat response and monitoring user interactions, they do not provide the hardware-backed key management or client-side encryption delivered by Cloud HSM for Google Workspace.
Cloud HSM for Google Workspace
Cloud HSM for Google Workspace
What Cloud HSM for Google Workspace is
Cloud HSM for Google Workspace is a fully managed, highly available encryption key management service that enables client-side encryption (CSE) for Google Workspace collaboration data, such as files in Google Drive and messages in Gmail. It uses envelope encryption backed by FIPS 140-2 Level 3 validated hardware security modules (HSMs), ensuring that cryptographic wrap and unwrap operations occur strictly inside the hardware boundary.
Client-Side Encryption with Cloud HSM
Sequence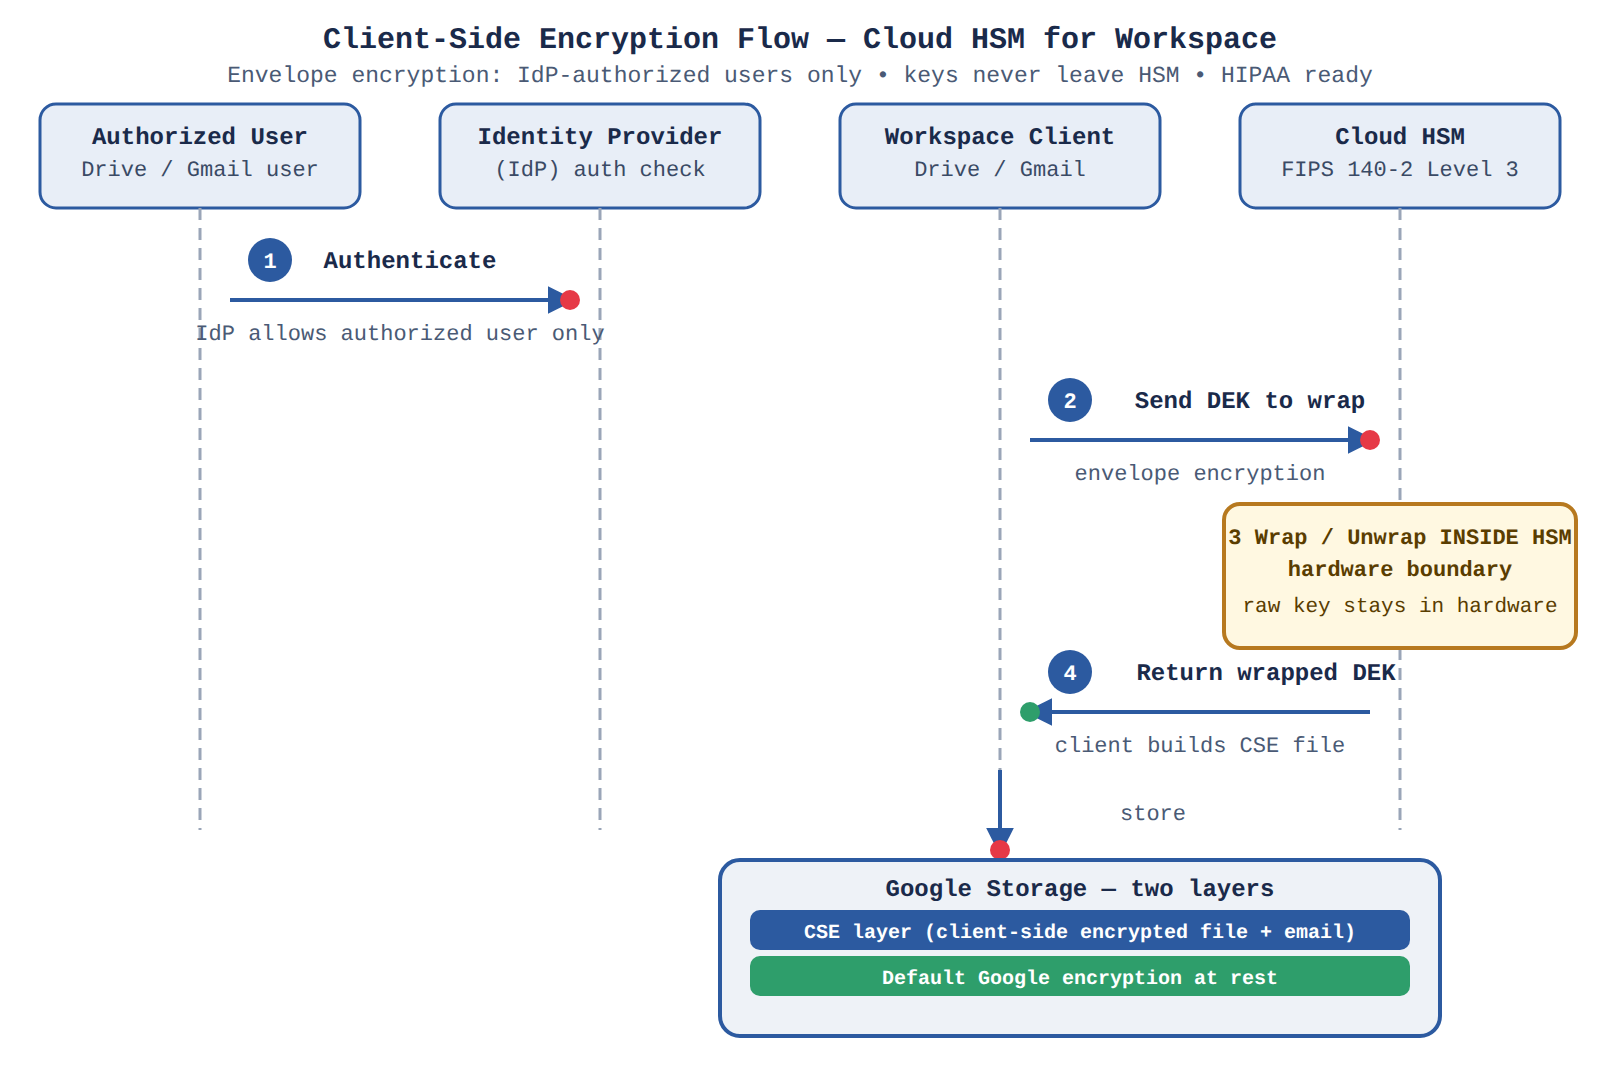
How it meets the requirements
- Adds client-side encryption (CSE) to collaboration tools: It applies an extra layer of encryption to Google Workspace files and emails before data is transmitted or stored, supplementing default cloud encryption.
- Protects keys in FIPS 140-2 Level 3 hardware: All encryption keys are hardware-backed and stored in FIPS 140-2 Level 3 compliant HSMs, where the raw key material never leaves the HSM protection boundary.
- Enforces verifiable user interactions and compliance: It integrates with the organization's identity provider (IdP) so that only explicitly authorized users can encrypt or decrypt sensitive files and emails, directly supporting strict regulatory standards such as HIPAA, FedRAMP, and PCI DSS.
Key advantages and capabilities
- Enhanced data control: Gives organizations direct control over their encryption keys while preserving seamless real-time collaboration in Google Workspace.
- Regulatory alignment: Helps organizations in regulated industries—such as healthcare, finance, and government—meet strict compliance mandates.
- Verifiable auditability: Writes comprehensive audit logs using Cloud Logging to record administrative activities and key access events—helping security teams verify who did what and when.
- Predictable cost model: Offers flat pricing that does not fluctuate based on the total number of users.
- Flexible key architecture: Supports both multi-tenant and single-tenant Cloud HSM keys.
Why this is optimal
Unlike general infrastructure security tools or administrative access logs, Cloud HSM for Google Workspace is purpose-built to secure employee connections and sensitive collaborations within Google Workspace through hardware-backed client-side encryption.
Access Approval
Access Approval
What Access Approval is and does
Access Approval is a Google Cloud privileged access management control that requires explicit customer approval before an authorized Google administrator or support engineer can access customer data during a support event or maintenance activity. When paired with Access Transparency, it provides verifiable oversight and logging of administrative interactions by Google personnel.
Why it doesn't meet the requirement
- No client-side encryption capabilities: Access Approval is an administrative access control workflow that governs Google support personnel; it does not encrypt Google Workspace files or emails.
- No HSM key management: It does not store cryptographic keys in FIPS 140-2 Level 3 hardware security modules or perform envelope encryption for end-user collaboration tools.
- Does not govern employee-to-employee file encryption: It regulates when Google staff can view customer data for support purposes rather than integrating with an identity provider (IdP) to decrypt client-side encrypted Workspace documents.
Key characteristics and limitations
- Explicit consent workflow: Sends an approval request to designated customer administrators whenever Google personnel need temporary access to resolve a support ticket.
- Integration with Access Transparency: Links approved access requests directly to Access Transparency logs, creating an auditable trail of administrative activity.
- Strict privilege verification: Ensures that even after a customer approves a request, the Google administrator's access is strictly privileged and time-bound.
This answer would be correct if
This option would be the right choice if the organization wanted to enforce a policy requiring its security team to explicitly review and approve requests before any Google Cloud support engineer could access their cloud environment during a troubleshooting session.
Additional context
Access Approval and Access Transparency are important pillars for establishing trusted transactions between an enterprise and its cloud provider. However, when the requirement specifically calls for encrypting Google Workspace files and emails using hardware-backed keys, Cloud HSM for Google Workspace is required.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 3,070 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalCloud Digital Leader
BigQuery, BigQuery ML, and Looker
Describe the transformation cloud and how it accelerates an organization’s digital transformation through app and infrastructure modernization, data democratization, people connections, and trusted transactions.
FundamentalCloud Digital Leader
Business Consequences of Security Incidents
Describe today’s top cybersecurity threats and business implications.
FundamentalCloud Digital Leader
Cloud Audit Logs vs Security Command Center
Differentiate between cloud security and traditional on-premises security.
FundamentalCloud Digital Leader
Replatforming to Cloud SQL for MySQL
Describe the ways that an organization can migrate or modernize their current database in the cloud.
FundamentalCloud Digital Leader
Cloud Vision API Features
Select which Google Cloud pre-trained API best applies to different business use cases, including: Natural Language API, Vision API, Cloud Translation API, Speech-to-Text API, and Text-to-Speech API.
FundamentalAssociate Data Practitioner
Cloud Composer vs Workflows vs Dataproc Workflow Templates
Select a data orchestration solution (e.g., Cloud Composer, scheduled queries, Dataproc Workflow Templates, Workflows) based on business requirements
Last updated