Fundamental
Prepare and test your skills
Fundamental
Prepare and test your skills
Using Predefined Roles for BigQuery Least Privilege
Free sample question, answered and explained below. The Associate Data Practitioner practice bank has 1,156 more like it. Try 10 free: instant score, no account.
A data analytics team is onboarding a new data analyst who needs to run SQL query jobs and view table data in BigQuery within a specific Google Cloud project. The team's security policy requires following the principle of least privilege by avoiding overly permissive access across other Google Cloud resources in the project.
Which IAM role approach should the administrator use to grant the required access?
Explanations
Assign the basic Editor role (roles/editor) at the project level.
Assign the basic Editor role (roles/editor) at the project level.
What the Editor basic role is
The Editor (roles/editor) role is a legacy basic role that grants extensive read, write, modify, and delete permissions for almost all resources across all Google Cloud services in a project.
Why it doesn't meet the requirement
- Severe over-privileging: Granting Editor gives the user full control to deploy, modify, and delete non-BigQuery resources such as virtual machines, databases, firewalls, and storage buckets across the entire project.
- Direct violation of security standards: It violates the organization's requirement to enforce least privilege and avoid excessive permissions.
Key characteristics of the Editor role
- Broad write access: Enables creating and destroying critical cloud infrastructure across services.
- Coarse management: Lacks granular controls needed for data governance and data segregation.
- Security risk: High potential for accidental resource deletion or administrative misconfiguration.
This answer would be correct if
A lead developer required comprehensive write access across all services within a dedicated non-production sandbox project to rapidly prototype and manage multi-service architectures.
Assign the basic Viewer role (roles/viewer) at the project level.
Assign the basic Viewer role (roles/viewer) at the project level.
What the Viewer basic role is
The Viewer (roles/viewer) role is a legacy basic role (primitive role) that grants broad read-only access across almost all Google Cloud services and resources residing within the assigned project.
Why it doesn't meet the requirement
- Violates least privilege: The Viewer role provides read access across Compute Engine instances, Cloud Storage buckets, Cloud SQL databases, networking configurations, and monitoring logs throughout the entire project, far exceeding the analyst's BigQuery-only scope.
- Lacks execution permissions: Running queries in BigQuery requires the ability to create and execute query jobs (
bigquery.jobs.create). The Viewer role alone does not provide sufficient permissions to run BigQuery jobs in the project.
Key limitations of basic roles
- Broad scope: Contains thousands of permissions spanning virtually every Google Cloud product.
- All-or-nothing model: Cannot restrict visibility to a single service or specific dataset.
- Production risk: Google explicitly advises against using basic roles in production environments due to excessive privilege exposure.
This answer would be correct if
A stakeholder required global, project-wide read-only visibility into all Google Cloud infrastructure components and configurations for general auditing without executing compute or analytics jobs.
Assign the basic Writer role (roles/writer) at the project level.
Assign the basic Writer role (roles/writer) at the project level.
What the Writer basic role is
The Writer (roles/writer) role is a broad basic role that contains read permissions plus state-modifying and creation permissions across most Google Cloud services.
Why it doesn't meet the requirement
- Overly permissive across services: Like other basic roles, Writer applies globally across numerous Google Cloud APIs and services rather than restricting access specifically to BigQuery.
- Unnecessary resource modification: It allows creating and changing resources in Compute Engine, Cloud Storage, and other non-data services that the analyst has no business need to interact with.
Key limitations of the Writer role
- Non-granular: Spans across multiple services rather than focusing on specific job tasks.
- Legacy/Broad model: Does not align with modern role-based access control (RBAC) practices for secure data platforms.
This answer would be correct if
An administrative user needed generic write capabilities across a wide spectrum of Google Cloud services where predefined roles or fine-grained access boundaries were not applicable.
Assign service-specific predefined roles, such as BigQuery Job User and BigQuery Data Viewer, instead of a basic role.
Assign service-specific predefined roles, such as BigQuery Job User and BigQuery Data Viewer, instead of a basic role.
What predefined roles are
Predefined roles in Google Cloud are granular, service-specific Identity and Access Management (IAM) roles created and maintained by Google. Unlike basic roles, which apply broadly across all Google Cloud services in a project, predefined roles bundle specific permissions tailored to distinct job functions and individual services like BigQuery, Cloud Storage, or Vertex AI.
How this meets the requirement
- Granular service access: Assigning BigQuery Job User (
roles/bigquery.jobUser) grants the exact permissions required to run query jobs (bigquery.jobs.create), while BigQuery Data Viewer (roles/bigquery.dataViewer) permits viewing datasets and tables without exposing unrelated services. - Enforces least privilege: By using predefined roles, the analyst receives only the permissions necessary for their analytical tasks, avoiding unintended access to Compute Engine, Cloud Storage, Cloud SQL, or project administrative settings.
- Scoped resource assignment: Predefined data roles can be bound at the dataset or table level, providing refined control over sensitive data assets.
Basic vs Predefined Role Scope
Set Relationship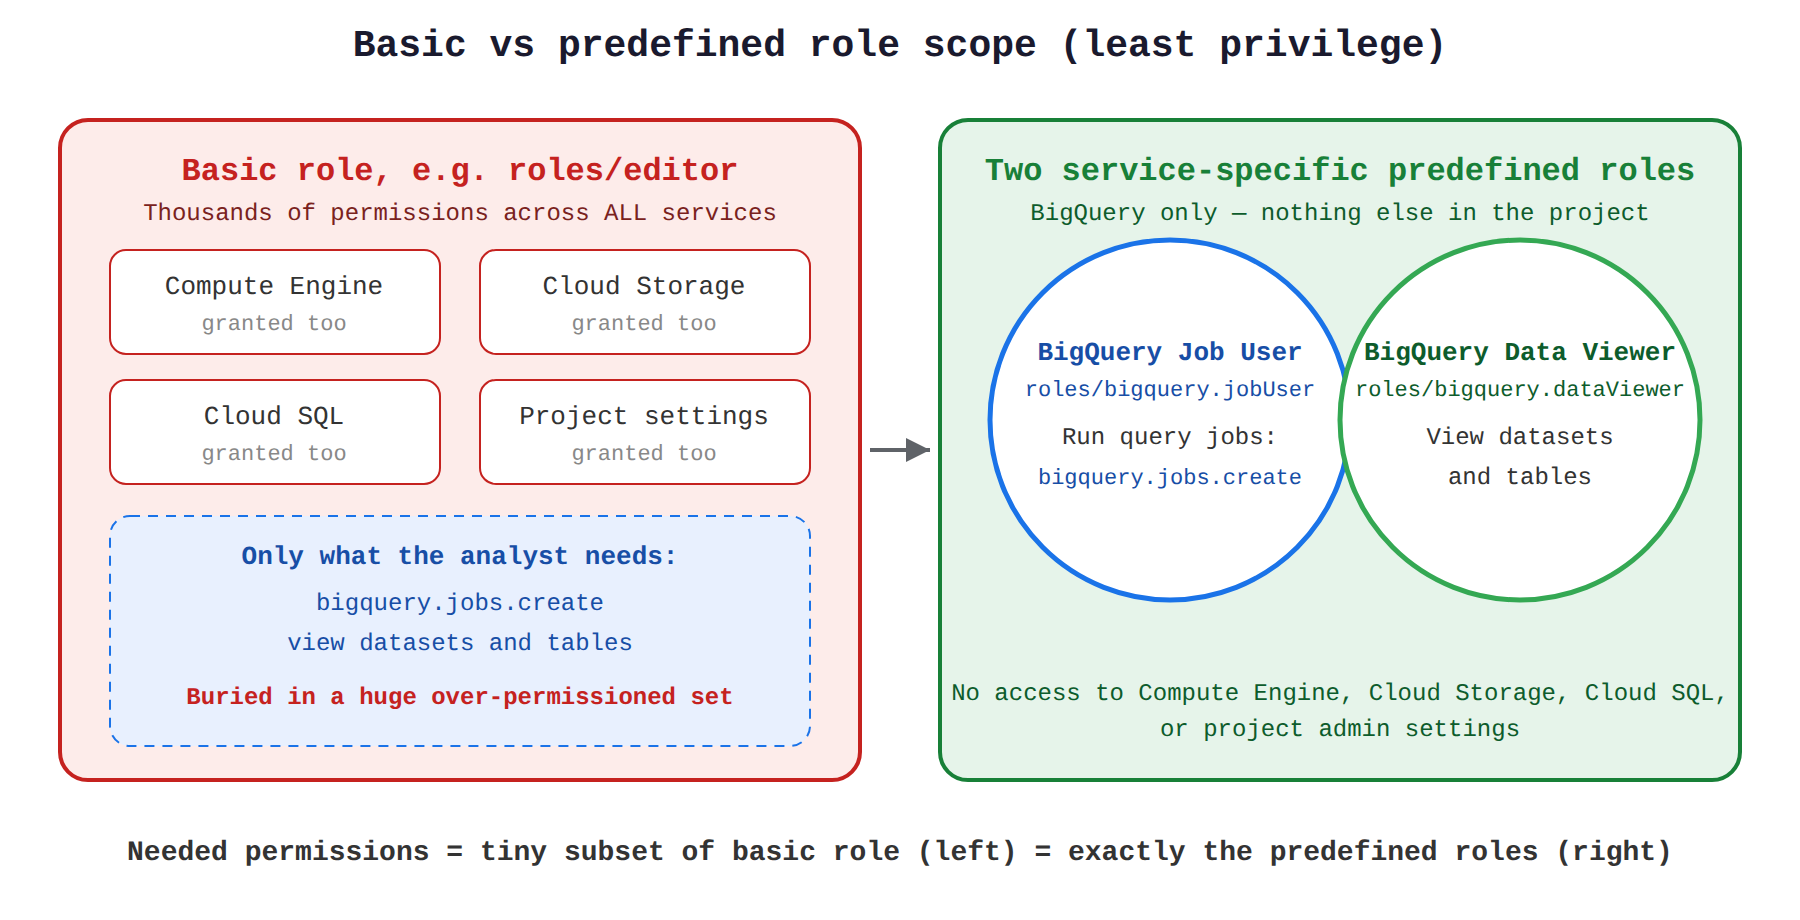
Key advantages of predefined roles
- Service-specific isolation: Limits access strictly to targeted APIs and operations.
- Maintained by Google: Automatically updated when new underlying API methods or features are added to the service.
- Audit compliance: Facilitates security audits by maintaining clear, predictable access boundaries.
- Reduced blast radius: Minimizes potential security impact if user credentials are leaked or compromised.
Why this is optimal
Using predefined roles directly aligns with Google Cloud security best practices. Basic roles grant sweeping permissions across hundreds of cloud services simultaneously, which violates enterprise governance and the principle of least privilege.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 1,156 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Data Practitioner
Cloud Storage Predefined Roles
Differentiate between basic roles, predefined roles, and permissions for data services (e.g., BigQuery, Cloud Storage)
FundamentalAssociate Data Practitioner
IAM Permissions Bundled into Roles
Differentiate between basic roles, predefined roles, and permissions for data services (e.g., BigQuery, Cloud Storage)
FundamentalAssociate Data Practitioner
LookML Field Presentation Parameters
Manipulate simple LookML parameters to modify a data model
FundamentalAssociate Data Practitioner
Transfer Appliance vs Storage Transfer Service
Choose the appropriate data transfer tool (e.g., Storage Transfer Service, Transfer Appliance)
FundamentalAssociate Data Practitioner
Dataform rowConditions Assertions
Assess data quality
AdvancedProfessional Cloud Security Engineer
STS Data Access Audit Logs
Configuring Google Cloud Directory Sync and implement single sign-on (SSO) with a third-party identity provider.
Last updated