Fundamental
Prepare and test your skills
Fundamental
Prepare and test your skills
IAM Roles Bundle Permissions for Least Privilege
Free sample question, answered and explained below. The Associate Data Practitioner practice bank has 1,156 more like it. Try 10 free: instant score, no account.
A data engineering team wants to allow a new team member to upload raw data files to a Google Cloud Storage bucket. Following the principle of least privilege, the team wants to ensure the user receives only the specific capability to write objects (such as storage.objects.create), without gaining unnecessary administrative control or wide access across the entire project.
Which statement accurately describes how Google Cloud IAM structures permissions and roles to fulfill this access requirement?
Explanations
Predefined roles automatically include all permissions for all Google Cloud services, requiring an explicit IAM deny policy to isolate specific actions.
Predefined roles automatically include all permissions for all Google Cloud services, requiring an explicit IAM deny policy to isolate specific actions.
What Predefined Roles and Deny Policies are:
Predefined roles are fine-grained, Google-managed roles tailored to specific services and job duties (e.g., Storage Object Creator, Storage Admin). IAM deny policies are rules that prevent principals from using specific permissions, overriding any granted allow roles.
Why it doesn't meet the requirement:
- Incorrect definition of predefined roles (✗): Predefined roles do not grant all permissions across all cloud services. Each predefined role contains a curated subset of permissions specific to a single service or set of tasks.
- Unnecessary complexity (✗): Least privilege is achieved by granting only the relevant predefined or custom role, rather than granting excessive access and trying to subtract permissions using deny policies.
Key characteristics and limitations:
- Predefined roles are maintainable and automatically updated by Google when new relevant APIs are added.
- Deny policies are used for guardrails (such as preventing anyone from deleting specific audit logs), not for basic day-to-day role scoping.
This answer would be correct if:
Every predefined role had universal administrative privileges and IAM followed a pure blacklist/subtractive permission model rather than a role-based allow model.
Basic roles like Editor or Owner must be granted at the project level because granular object permissions cannot be isolated into service-specific roles.
Basic roles like Editor or Owner must be granted at the project level because granular object permissions cannot be isolated into service-specific roles.
What Basic Roles are:
Basic roles (previously known as primitive roles: Owner, Editor, and Viewer) are broad, legacy roles that existed prior to IAM. They grant blanket access across almost all Google Cloud services within an entire project.
Why it doesn't meet the requirement:
- Violates least privilege (✗): Granting a basic role like
Editorgives extensive modification and deletion rights to virtually all services in the project, which directly contradicts least-privilege security requirements. - False premise regarding isolation (✗): Granular object permissions can easily be isolated using service-specific predefined roles (such as
roles/storage.objectCreator) or custom roles.
Key characteristics and limitations:
- Basic roles are coarse-grained and apply project-wide.
- They lack the specificity required for data governance and production security baselines.
- Google Cloud strongly recommends using predefined or custom roles instead of basic roles for production workloads.
This answer would be correct if:
A scenario required broad, unrestricted development privileges across all computing, storage, and networking resources in a disposable sandbox environment.
Individual permissions are attached directly to the user identity in an IAM policy, while roles are used solely to organize users into administrative groups.
Individual permissions are attached directly to the user identity in an IAM policy, while roles are used solely to organize users into administrative groups.
What this option describes:
This option incorrectly asserts that Google Cloud IAM allows direct attachment of standalone individual permissions (like storage.objects.create) directly to a user's identity in an IAM policy.
Why it doesn't meet the requirement:
- Architectural inaccuracy (✗): Google Cloud IAM does not support direct permission assignment to principals. IAM policies define bindings strictly between principals and roles.
- Mischaracterization of roles (✗): Roles are not containers for grouping users; Google Groups or Workspace groups organize users, while IAM roles package permissions together.
Key characteristics and limitations:
- Permissions define what specific action can be taken (e.g., creating an object).
- Principals define who is requesting access (e.g., a user, group, or service account).
- IAM policies connect who (principal) with what (role containing permissions) on which resource.
This answer would be correct if:
Google Cloud IAM operated on an Access Control List (ACL) model that permitted assigning raw API actions directly to user entities without utilizing roles as an intermediary abstraction.
Individual permissions cannot be granted directly to principals; instead, permissions are bundled into predefined or custom roles that are assigned to the principal.
Individual permissions cannot be granted directly to principals; instead, permissions are bundled into predefined or custom roles that are assigned to the principal.
What IAM Roles and Permissions Are:
In Google Cloud Identity and Access Management (IAM), permissions are the fundamental, granular units of access that define discrete actions allowed on a resource (for example, storage.objects.create or storage.buckets.list). Roles are organized collections or bundles of one or more permissions designed to represent specific operational responsibilities.
How it meets the access control requirement:
- Permission bundling (✓): Google Cloud does not allow administrators to assign atomic permissions directly to a user account, group, or service account. Access must always be granted via a role.
- Least privilege alignment (✓): To grant specific capabilities like object creation without unnecessary broad access, administrators can select a focused predefined role (such as Storage Object Creator,
roles/storage.objectCreator) or build a custom role containing only the necessary permissions and bind it at the bucket level. - Resource-level binding (✓): Roles can be granted at granular resource levels (such as a specific bucket or managed folder) rather than broad project-wide scopes.
Permissions Bundled Into Roles
Set Relationship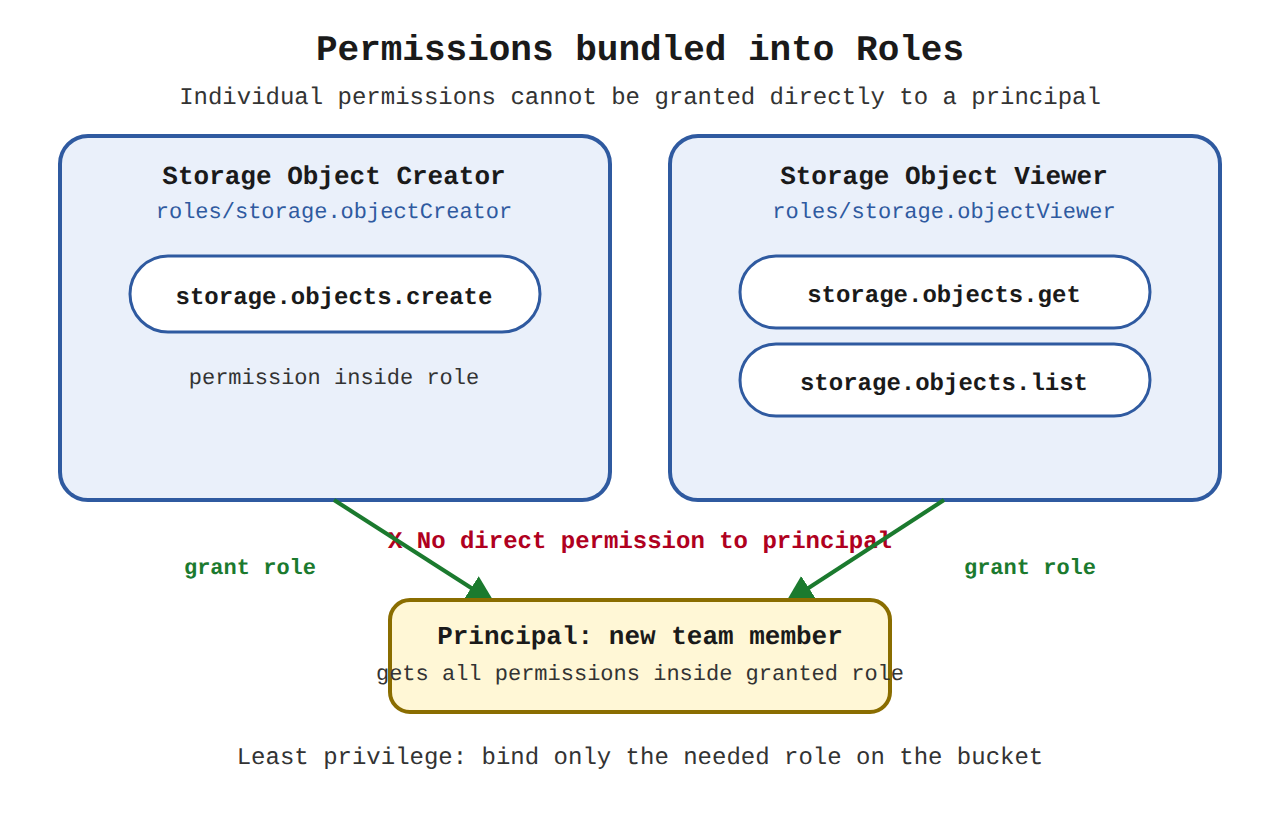
Key advantages of IAM role composition:
- Consistent governance: Grouping permissions into logical roles simplifies auditing and policy management across cloud resources.
- Granular control: Predefined roles allow fine-grained access matching real-world job functions without excessive privileges.
- Customizability: Organizations can assemble custom roles tailored strictly to unique internal security policies.
- Scalable administration: Managing access through role bindings to groups or identities avoids permission sprawl.
Why this is optimal:
Understanding that permissions exist as the underlying mechanism packaged within roles is foundational in Google Cloud. It ensures administrators use tailored predefined or custom roles at the correct resource hierarchy level rather than defaulting to overly broad basic roles.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 1,156 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Data Practitioner
Cloud Storage Predefined Roles
Differentiate between basic roles, predefined roles, and permissions for data services (e.g., BigQuery, Cloud Storage)
FundamentalAssociate Data Practitioner
IAM Predefined Roles vs Basic Roles
Differentiate between basic roles, predefined roles, and permissions for data services (e.g., BigQuery, Cloud Storage)
FundamentalAssociate Data Practitioner
BigQuery ML K-means Clustering
Execute SQL to create, train, and evaluate models using BigQuery ML
FundamentalAssociate Data Practitioner
ETL with Dataflow Pre-Load Transformations
Differentiate between different data manipulation methodologies (e.g., ETL, ELT, ETLT)
FundamentalAssociate Data Practitioner
Dataform rowConditions Assertions
Assess data quality
AdvancedProfessional Data Engineer
MIG Autohealing vs Load Balancer Health Checks
Designing system for fault tolerance and managing restarts
Last updated