Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Service Accounts for Automated Compute Engine Workloads
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your company is deploying an automated data processing application on a Compute Engine virtual machine (VM) in Google Cloud. The application needs to read source files from and write processed results to a Cloud Storage bucket without requiring human user interaction or personal login credentials.
Which IAM principal type should you create and grant access to for this application workload?
Explanations
A Service Account
A Service Account
What a Service Account Is
A service account is a special type of Google Cloud identity intended for applications, compute workloads, and virtual machines rather than individual human users. It is identified by a unique email address (such as custom-app@project-id.iam.gserviceaccount.com) and allows programmatic tasks to authenticate and call Google Cloud APIs securely.
How It Meets the Requirements
- Non-human application authentication: Service accounts are designed explicitly for workloads running on compute resources (such as Compute Engine VMs) to authenticate automatically without interactive human login.
- Direct IAM role assignment: You can grant IAM roles (such as
roles/storage.objectAdmin) directly to the service account, giving the VM instance only the permissions necessary to access the specified Cloud Storage bucket. - Least privilege and automation: By attaching the service account directly to the Compute Engine instance, the application automatically receives short-lived credentials to execute storage operations safely.
Key Advantages and Capabilities
- No hardcoded credentials: Attaching a service account to a VM eliminates the need to store passwords or API keys in code.
- Dual nature (Principal and Resource): Service accounts act as principals that can hold permissions, but they also function as resources that authorized administrators can manage.
- Fine-grained access control: Service accounts can be assigned minimal predefined or custom roles on specific resources.
- Lifecycle management: Service accounts can be created, updated, disabled, or deleted independently of individual user accounts.
Why This Is Optimal
Using a service account is Google's recommended practice for workload identities. It isolates application permissions from human personnel, adheres to the principle of least privilege, and prevents operational disruptions when employee accounts change or are deprovisioned.
A Google Group
A Google Group
What a Google Group Is
A Google Group is a named collection of Google Accounts and service accounts identified by a single group email address (such as cloud-engineers@example.com).
Why It Doesn't Meet the Requirement
- Not an authenticating identity: Google Groups do not have login credentials or private keys; they cannot authenticate or be attached directly to a Compute Engine virtual machine.
- Organizational tool rather than a workload identity: A group is used to simplify permission management across multiple human users, not to provide an execution identity for software.
Key Characteristics and Limitations
- Bulk permission management: Granting an IAM role to a Google Group automatically grants that role to all members in the group.
- No authentication capability: Applications cannot log in or generate access tokens as a Google Group.
- Convenience wrapper: Adding or removing users from the group updates their access across all assigned resources without modifying individual IAM policies.
This Answer Would Be Correct If
You had a team of multiple cloud operators or analysts who all required identical read access to the Cloud Storage bucket and you wanted to manage their access collectively.
Additional Context
While a service account can be added as a member of a Google Group, the application itself still runs as a service account.
A Google Account
A Google Account
What a Google Account Is
A Google Account represents an individual human user (such as a developer, administrator, or employee) authenticated through an @gmail.com address or a corporate email managed by Cloud Identity or Google Workspace.
Why It Doesn't Meet the Requirement
- Designed for humans, not applications: Google Accounts require interactive human authentication (passwords, multi-factor authentication, single sign-on) and are not intended for automated background processes.
- Security risk: Using an individual user's credentials for an automated application creates security vulnerabilities, requires storing user credentials on the VM, and ties infrastructure availability to an individual person's account status.
Key Characteristics and Limitations
- Individual identity: Represents a single human interacting with Google Cloud services via the web console or command-line tools.
- Lifecycle dependency: If an employee leaves the company and their Google Account is suspended or deleted, any automated workload depending on that account will immediately fail.
- Audit trail inaccuracy: Activity logs will attribute automated machine actions to a specific human user rather than the workload.
This Answer Would Be Correct If
A developer or system administrator needed personal access to log into the Google Cloud console or run gcloud CLI commands from their workstation.
Additional Context
Google Accounts should be used exclusively for human users who require individual access and interactive sign-in sessions.
A Google Workspace Domain
A Google Workspace Domain
What a Google Workspace Domain Is
A Google Workspace domain represents all user accounts created within an organization's registered internet domain name (such as example.com).
Why It Doesn't Meet the Requirement
- Excessively broad scope: Granting permissions to an entire domain grants access to every single user account under that domain, violating the principle of least privilege.
- Cannot be assigned to a workload: A domain is not an execution identity and cannot be attached to a Compute Engine instance for automated API access.
- Does not include service accounts: Service accounts do not inherently belong to a Google Workspace domain in a way that allows them to inherit domain-wide access grants.
Key Characteristics and Limitations
- Domain-wide principal set: Represents all current and future human users within an organization's directory.
- High blast radius: Assigning roles at the domain level exposes cloud resources to every employee across the entire enterprise.
- Unsuitable for headless workloads: VMs and applications require distinct service credentials, not broad enterprise user directory associations.
This Answer Would Be Correct If
Your organization wanted to make general corporate documentation or non-sensitive internal reference data accessible to every employee in the company directory simultaneously.
Additional Context
Google Workspace domains are used for organization-wide identity management and collaboration sharing, never for workload-level compute permissions.
Try the scenario
Choosing the Right IAM Principal for an Automated VM Workload
Change the inputs and watch how the outcome changes.
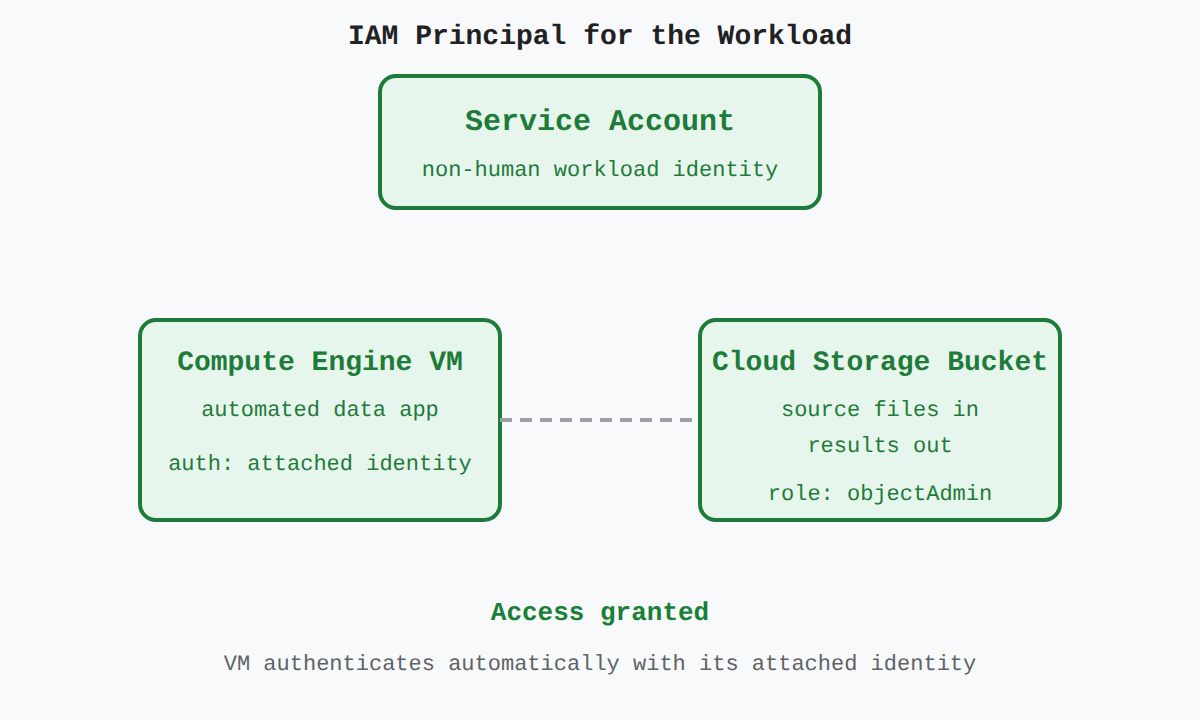
Change the principal type and workload context to see whether the application can reach the Cloud Storage bucket without human login.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Google Cloud Predefined IAM Roles
Granting members Identity and Access Management (IAM) roles within a project
FundamentalAssociate Cloud Engineer
gcloud projects add-iam-policy-binding
Granting members Identity and Access Management (IAM) roles within a project
FundamentalAssociate Cloud Engineer
Cloud Run Min-Instances vs Max-Instances
Configuring autoscaling for a Cloud Run application
FundamentalAssociate Cloud Engineer
External Application Load Balancer Frontend Backend Configuration
Choosing and deploying load balancers
FundamentalAssociate Cloud Engineer
Cloud Run Functions with Functions Framework
Selecting appropriate compute choices for a given workload (e.g., Compute Engine, Google Kubernetes Engine [GKE], Cloud Run, Cloud Run functions, Knative serving)
FundamentalGenerative AI Leader
Gemini Imagen Code Assist Modality Mapping
Recognizing the different types of gen AI solutions (e.g., text generation, image generation, code generation, personalized user needs)
Last updated