Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Routing ERROR Severity Logs to BigQuery
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your security operations team needs to perform advanced SQL analytics on critical security events. You are tasked with routing log entries generated across your Google Cloud project so that only log entries with a severity level of ERROR or higher are exported to a dedicated BigQuery dataset.
What should you configure in Cloud Logging to meet this requirement?
Explanations
Configure an archetype storage spec in Manufacturing Data Engine to materialize metadata into BigQuery
Configure an archetype storage spec in Manufacturing Data Engine to materialize metadata into BigQuery
What Manufacturing Data Engine Sinks Are
Manufacturing Data Engine (MDE) is an industry-specific data solution designed to ingest, contextualize, and store industrial telemetry and IoT sensor time-series data using predefined storage specifications.
Why It Doesn't Meet the Requirement
- Incorrect Service: MDE storage specifications manage IoT and industrial machine telemetry tags, not general Google Cloud infrastructure and application event logs.
- Unrelated to Cloud Logging: Cloud Logging manages platform logs, audit logs, and application standard output across GCP services, operating completely independently from Manufacturing Data Engine archetypes.
- Missing Severity Filtering: MDE tag persistence models persist numeric or discrete telemetry values rather than evaluating Cloud Logging severity attributes.
Key Characteristics and Limitations
- Tailored specifically for industrial IoT and sensor data persistence.
- Configured via MDE archetypes, data types, and tag definitions.
- Does not act as a central log export router for Google Cloud project logs.
This Answer Would Be Correct If
The objective was to store industrial IoT machine tags and factory sensor metrics into BigQuery and Bigtable using Manufacturing Data Engine.
Create a Log Router sink with an inclusion filter set to severity >= ERROR and specify the BigQuery dataset as the destination
Create a Log Router sink with an inclusion filter set to severity >= ERROR and specify the BigQuery dataset as the destination
What Cloud Logging Sinks and the Log Router Are
In Google Cloud, the Log Router checks every incoming log entry against configured log sinks to determine where logs should be sent. A log sink consists of a query filter (inclusion filter), an optional set of exclusion filters, and a supported destination (such as a BigQuery dataset, Cloud Storage bucket, Pub/Sub topic, or another Cloud Logging bucket).
How It Meets the Requirements
- Exporting to BigQuery: The sink definition allows you to select a BigQuery dataset as the target destination (
bigquery.googleapis.com/projects/[PROJECT_ID]/datasets/[DATASET_ID]), enabling native SQL analytics on exported log data. - Filtering by Severity: By defining an inclusion filter such as
severity >= ERROR, the Log Router evaluates incoming entries in real time and routes only logs matchingERROR,CRITICAL,ALERT, orEMERGENCYseverities to BigQuery. - Efficiency and Cost Control: Logs below the
ERRORthreshold (such asINFO,NOTICE, orWARNING) do not match the sink's filter criteria and are not exported to BigQuery, avoiding unnecessary ingestion and storage costs.
Severity Threshold Inclusion Filter
Set Relationship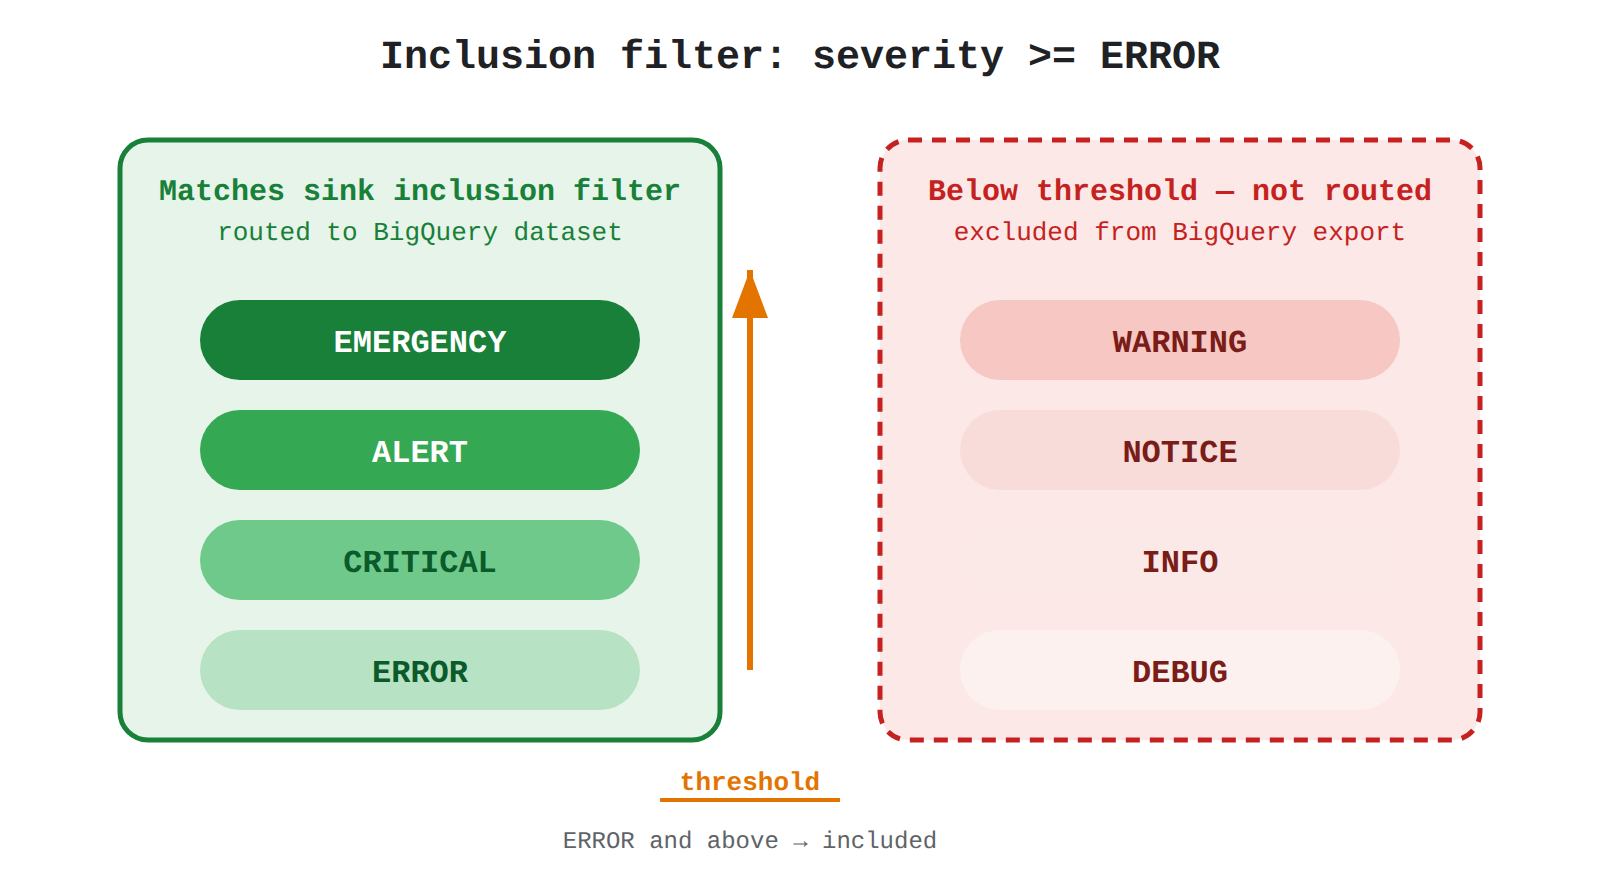
Key Advantages and Capabilities
- Real-time streaming: Log Router sinks stream log entries directly to supported destinations as soon as they are ingested.
- Flexible filtering: Sinks use Logging query language expressions to match resource types, log names, payload fields, and severity levels.
- Multiple destinations: The same logs can simultaneously match multiple sinks to route data to BigQuery for analytics and Cloud Storage for long-term archival.
- Fine-grained exclusion: Sinks support exclusion filters to selectively drop high-volume or redundant events before routing.
Why This Is Optimal
Creating a Log Router sink with an inclusion filter is the standard, native mechanism in Google Cloud to filter and export log records to analytical storage such as BigQuery without requiring intermediate compute resources or custom code.
Create an alerting policy in Cloud Monitoring with an exclusion filter and set the notification channel to the BigQuery dataset
Create an alerting policy in Cloud Monitoring with an exclusion filter and set the notification channel to the BigQuery dataset
What Cloud Monitoring Alerting Policies Are
Cloud Monitoring alerting policies monitor metric thresholds or log-based error conditions and trigger notifications when predefined conditions are met. Notification channels include email, SMS, PagerDuty, Slack, Pub/Sub, and webhooks.
Why It Doesn't Meet the Requirement
- Invalid Export Mechanism: Cloud Monitoring alerting policies are designed to send incident alert notifications to responders, not stream high-volume structured log streams into BigQuery tables.
- Unsupported Notification Destination: A BigQuery dataset is a data warehouse repository and cannot be configured directly as a notification channel for alert incidents.
- Architectural Misalignment: Alert policies evaluate aggregated metrics or log occurrences to generate alerts, whereas the requirement is to export full log records for SQL analysis.
Key Characteristics and Limitations
- Alerting policies fire notifications when incidents open, update, or close.
- Notification channels deliver alert metadata rather than full, raw log records.
- Metric-based alerts do not maintain the full JSON payload of individual log entries.
This Answer Would Be Correct If
The scenario required notifying an incident response team or sending a webhook message whenever the frequency of error logs exceeded a predefined operational threshold.
Configure a subnet VPC Flow Logs filter expression with filterExpr set to severity >= ERROR targeting BigQuery
Configure a subnet VPC Flow Logs filter expression with filterExpr set to severity >= ERROR targeting BigQuery
What VPC Flow Logs and Subnet Filtering Are
VPC Flow Logs record network traffic flows sent and received by Compute Engine VM network interfaces within Virtual Private Cloud (VPC) subnets. The filterExpr parameter allows administrators to sample or restrict which network packets generate flow records based on protocol, IP addresses, or ports.
Why It Doesn't Meet the Requirement
- Scope Limitation: VPC Flow Logs only capture network metadata (e.g., source IP, destination IP, port, bytes, packets). They do not capture application, system, or security audit logs.
- Invalid Severity Filtering: VPC Flow Logs do not contain a
severityfield such asERRORorINFO; network records represent packet metadata rather than application severity levels. - Direct Export Unavailable: VPC Flow Logs are written into Cloud Logging; they cannot be configured at the subnet level to bypass Cloud Logging and export directly into BigQuery.
Key Characteristics and Limitations
- Captures layer 3 and layer 4 network traffic flow metadata only.
- Filter expressions at the subnet level evaluate attributes like
src_ip,dest_port, and protocol, not log severity. - Flow logs must still pass through the Log Router in Cloud Logging to reach external sinks.
This Answer Would Be Correct If
The goal was to filter network flow metadata for a specific subnet by IP address or TCP/UDP port before writing flow logs into Cloud Logging.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
logging.logEntries.create Permission
Exporting logs to external systems (e.g., on-premises, BigQuery)
FundamentalAssociate Cloud Engineer
Database Center Analyze System Performance
Using Database Center to manage the Google Cloud database fleet
FundamentalAssociate Cloud Engineer
Predefined vs Custom IAM Roles
Managing the various role types and defining custom IAM roles (e.g., basic, predefined, custom)
FundamentalAssociate Cloud Engineer
Artifact Registry Docker Image URI Format
Deploying a containerized application to GKE
FundamentalAssociate Cloud Engineer
BigQuery Multi-Region Location Redundancy
Maintaining multi-region redundancy across data solutions
AdvancedProfessional Cloud Security Engineer
Workforce Identity Federation gcloud Login Config
Configuring Workforce Identity Federation
Last updated