Diagram
DNSSEC Validation Sequence
Sequence
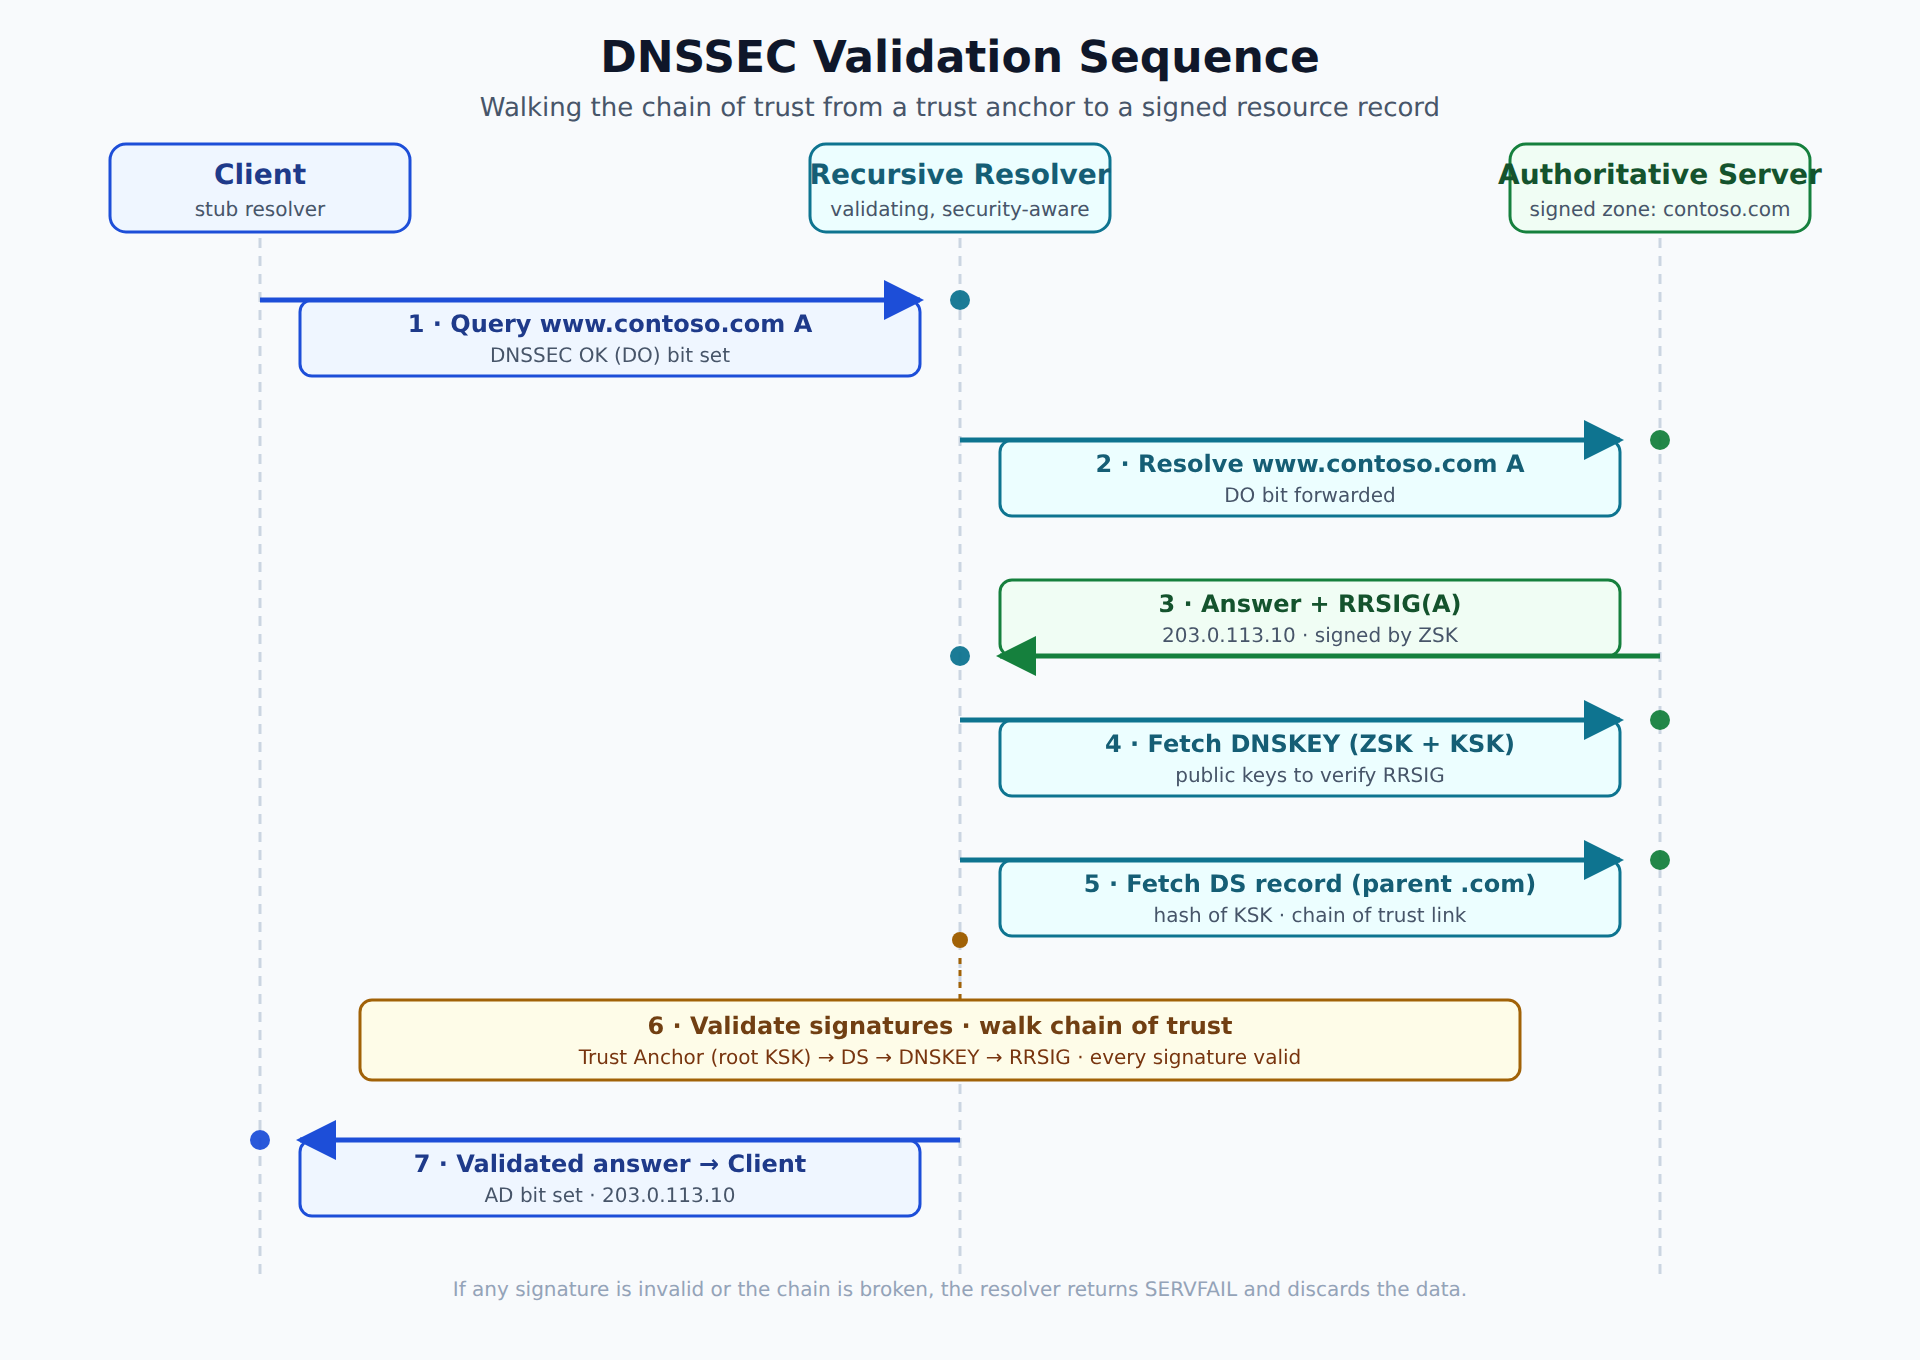
A sequence diagram showing how a client query with the DO bit flows through a recursive resolver, which walks the chain of trust from a trust anchor through DS and DNSKEY records to validate RRSIG signatures before returning the answer to the client.
In the Domain
Establishing Trust with Anchors and Validation
For a DNS resolver to begin validating DNSSEC-signed responses, it needs a starting point of trust called a Trust Anchor. This is a pre-configured public key (often the KSK of a top-level zone like the root) that the resolver inherently trusts. The validation process checks the digital signatures in a response, walking the chain of trust from the anchor down to the specific record. If every signature is valid, the resolver delivers the answer to the client. If the chain is broken or a signature is invalid, the resolver returns a failure (SERVFAIL) and does not provide the potentially fake data.
Domain 6 of 6
Implement Domain Name System Security Extensions
Read the Domain summaryPractice this Domain
2 practice questions
Practice this DomainLast updated