Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Cross-Project Feature Store Ingestion with Service Agents
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An enterprise maintains a multi-project architecture on Google Cloud. Raw source data is stored in BigQuery tables within a dedicated data warehouse project (project-data), while the machine learning platform team manages a Vertex AI Feature Store instance in a separate project (project-ml).
You need to configure access control so that the Vertex AI Feature Store in project-ml can ingest batch feature data from BigQuery in project-data. In addition, your organization's security policy requires that IT/DevOps administrators who configure and scale the Feature Store infrastructure cannot read or write actual feature values.
Which identity and access management (IAM) configuration should you implement?
Explanations
Grant the default Compute Engine service account from project-ml the roles/bigquery.admin role in project-data, and assign the roles/aiplatform.featurestoreAdmin role to the IT/DevOps administrators in project-ml.
Grant the default Compute Engine service account from project-ml the roles/bigquery.admin role in project-data, and assign the roles/aiplatform.featurestoreAdmin role to the IT/DevOps administrators in project-ml.
What the Option Is/Does
This approach grants the Compute Engine default service account broad administrative access to BigQuery in the source data project and assigns the full roles/aiplatform.featurestoreAdmin role to the DevOps team.
Why It Doesn't Meet the Requirement
- Incorrect Identity for Managed Ingestion: Vertex AI Feature Store uses the dedicated Vertex AI Service Agent (
@gcp-sa-aiplatform.iam.gserviceaccount.com)—not the Compute Engine default service account—to perform backend ingestion tasks from BigQuery. - Violation of Least Privilege / Security Policy: The
roles/aiplatform.featurestoreAdminrole includes full read and write permissions over featurestore contents (aiplatform.features.*and data operations), directly violating the policy that prevents IT/DevOps from reading or writing feature values.
Key Characteristics and Limitations
- Default service accounts should generally not be used for specialized managed AI platform tasks.
- Granting admin roles over entire services introduces significant data exposure and governance risks.
This Answer Would Be Correct If
DevOps engineers were required to manage the entire data lifecycle including schema updates, feature value modification, and ad-hoc data deletion, and if workloads ran inside self-managed Compute Engine virtual machines.
Grant the roles/aiplatform.featurestoreDataWriter role to the IT/DevOps administrators in project-ml, and grant the Vertex AI Service Agent from project-data read permissions in project-ml.
Grant the roles/aiplatform.featurestoreDataWriter role to the IT/DevOps administrators in project-ml, and grant the Vertex AI Service Agent from project-data read permissions in project-ml.
What the Option Is/Does
This configuration assigns data-writing privileges to IT/DevOps administrators and attempts to authorize the service agent belonging to the data project (project-data) instead of the consuming project.
Why It Doesn't Meet the Requirement
- Wrong Role Assignment: The
roles/aiplatform.featurestoreDataWriterrole is meant for data engineers and automated pipelines that write and ingest feature values into the store. It violates the constraint that DevOps administrators must not have data write or modification access. - Incorrect Service Agent Direction: The ingestion job is initiated and managed by
project-ml, which means the service agent residing inproject-mlneeds permissions onproject-data, not vice-versa.
Key Characteristics and Limitations
roles/aiplatform.featurestoreDataWritergrants write access to entity data and features rather than infrastructure instance management.- Granting permissions to the incorrect project's service agent will result in HTTP 403 Forbidden errors when Vertex AI tries to read BigQuery tables.
This Answer Would Be Correct If
The DevOps team were responsible for creating and writing feature values directly, and the featurestore resided in project-data pulling data from project-ml.
Assign the roles/aiplatform.user role to IT/DevOps administrators in project-ml, and configure a VPC Network Peering connection between project-data and project-ml to bypass IAM authorization.
Assign the roles/aiplatform.user role to IT/DevOps administrators in project-ml, and configure a VPC Network Peering connection between project-data and project-ml to bypass IAM authorization.
What the Option Is/Does
This option suggests using VPC Network Peering to bypass IAM checks for BigQuery data ingestion while granting the broad roles/aiplatform.user role to the infrastructure team.
Why It Doesn't Meet the Requirement
- Misunderstanding of Google Cloud IAM vs. Networking: VPC Network Peering provides RFC 1918 private network connectivity between VPC networks; it does not bypass or replace IAM authorization for Google Cloud managed APIs like BigQuery and Vertex AI.
- Overly Broad Role: The
roles/aiplatform.userrole allows users to create and manage various AI workloads and resources without restricting data-level access to feature values in the manner required by the security policy.
Key Characteristics and Limitations
- BigQuery and Vertex AI API calls are authenticated and authorized via IAM, regardless of underlying network topology.
- Network peering cannot substitute for proper IAM service agent permissions on source datasets.
This Answer Would Be Correct If
The workload involved private Compute Engine VM-to-VM communication over internal IP addresses rather than Google Cloud managed API data integration.
Grant the Vertex AI Service Agent (service-PROJECT_NUMBER@gcp-sa-aiplatform.iam.gserviceaccount.com) from project-ml read access to the BigQuery datasets in project-data, and assign the roles/aiplatform.featurestoreInstanceCreator role to the IT/DevOps administrators in project-ml.
Grant the Vertex AI Service Agent (service-PROJECT_NUMBER@gcp-sa-aiplatform.iam.gserviceaccount.com) from project-ml read access to the BigQuery datasets in project-data, and assign the roles/aiplatform.featurestoreInstanceCreator role to the IT/DevOps administrators in project-ml.
What Vertex AI Service Agents and Feature Store IAM Roles Are
Vertex AI Feature Store acts on behalf of users to execute background tasks—such as batch ingestion and feature serving—using a Google-managed service agent with the format service-PROJECT_NUMBER@gcp-sa-aiplatform.iam.gserviceaccount.com. In addition, Vertex AI provides fine-grained predefined IAM roles designed for distinct organizational personas, including administrators, data scientists, and DevOps personnel.
How It Meets the Requirements
- Cross-Project Ingestion: By default, the Vertex AI service agent only has access to resources inside its own host project (
project-ml). To import batch data across project boundaries fromproject-data, the service agent ofproject-mlmust be explicitly granted read permissions (such asroles/bigquery.dataViewerandroles/bigquery.jobUser) on the source BigQuery datasets. - Separation of Duties (Least Privilege): Assigning the
roles/aiplatform.featurestoreInstanceCreatorrole allows IT/DevOps engineers to provision, tune, and maintain featurestores without granting them read or write permissions to the sensitive feature data stored inside.
Cross-Project Least-Privilege Feature Ingestion
System Architecture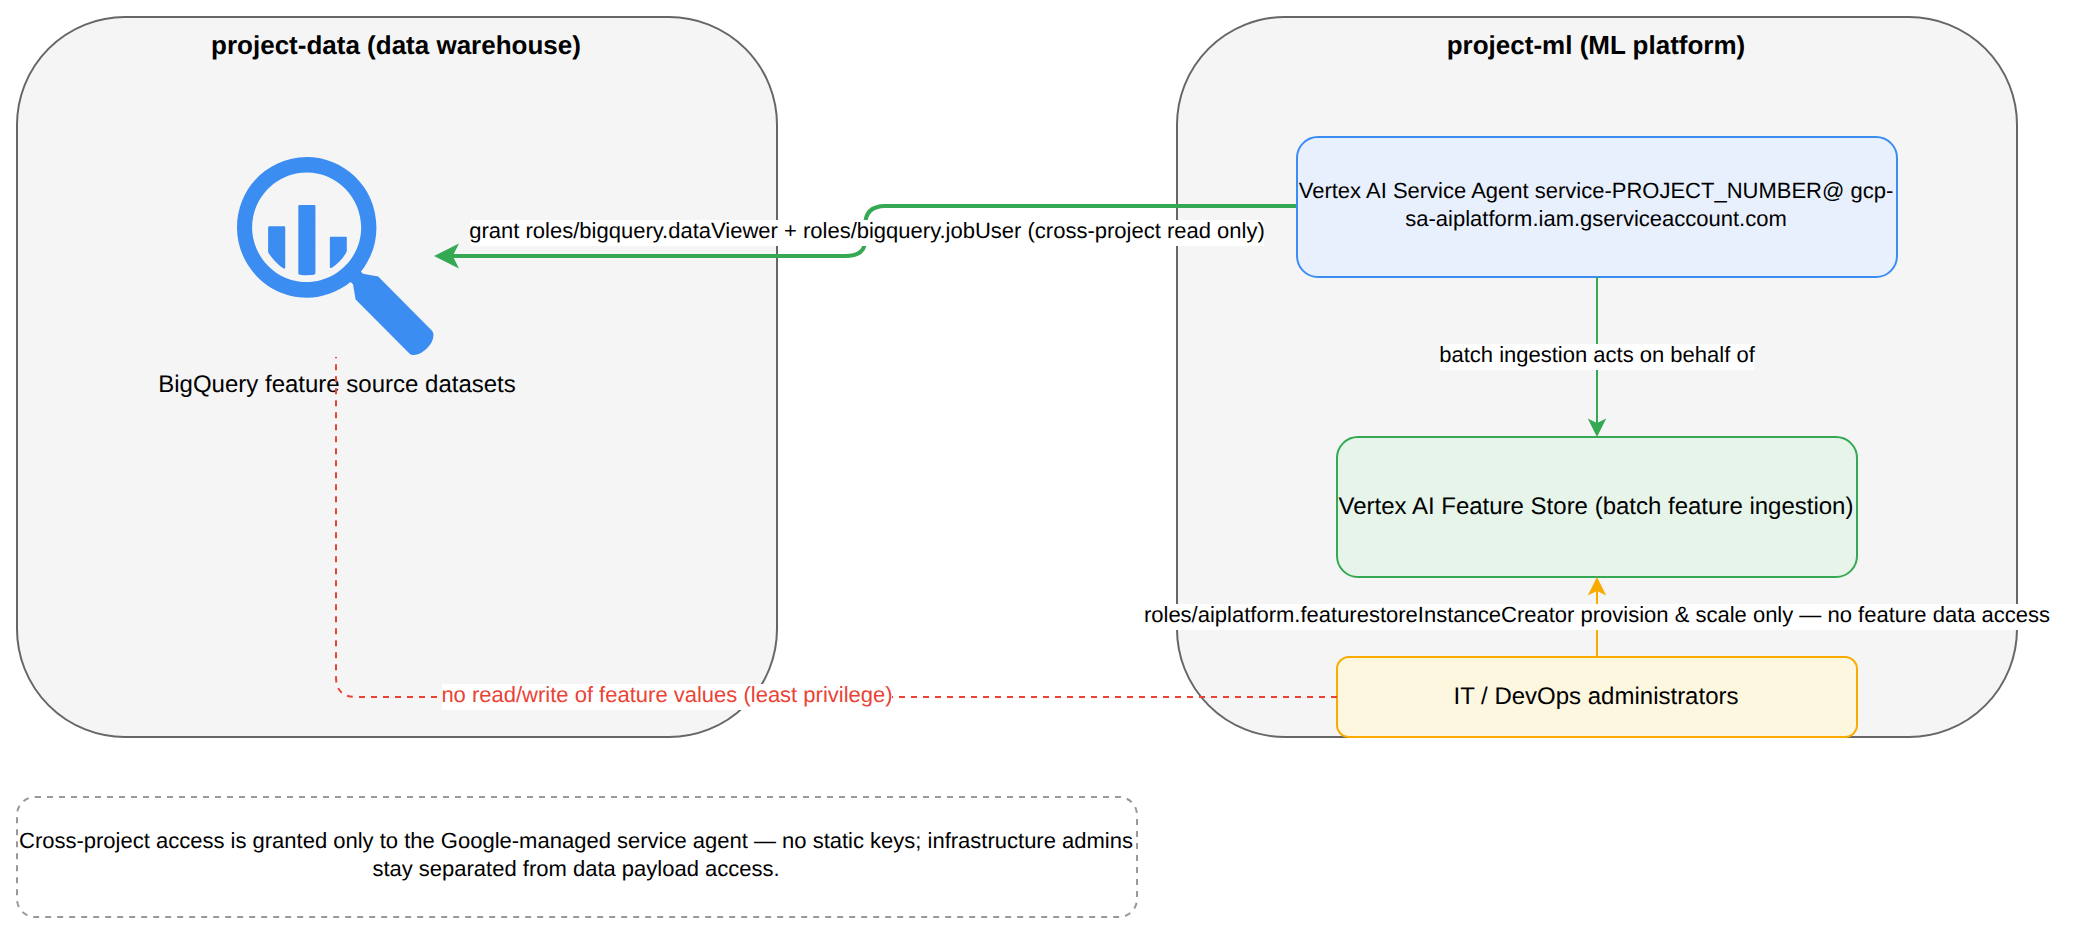
Key Advantages and Capabilities
- Automated Service-to-Service Authorization: Eliminates the need to generate, manage, and rotate static service account keys for ingestion jobs.
- Granular Data Isolation: Ensures infrastructure engineers can scale online serving nodes and adjust configurations while upholding compliance standards against unauthorized data access.
- Seamless Multi-Project Governance: Centralizes ML feature management while preserving isolated storage perimeters across independent data warehouse environments.
Why This Is Optimal
This pattern establishes standard least-privilege principles by separating infrastructure operations from data payload access and delegating cross-project ingestion authority strictly to the Google-managed Vertex AI service agent.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
BigQuery to Vertex AI Dataset Import
Preparing for Vertex AI data integration
IntermediateProfessional Cloud Architect
Vertex AI Forecasting Data Format Requirements
Preparing for Vertex AI data integration
IntermediateProfessional Cloud Architect
Event-Driven Vertex AI Pipeline Triggering
Using Vertex AI pipelines to automate and orchestrate the ML lifecycle
IntermediateProfessional Cloud Architect
Vertex AI Agent Engine Grounding and Integration
Google Cloud AI and machine learning solutions (e.g., Gemini LLMs, Agent Builder, Model Garden, Gemini models, and AI Hypercomputer)
IntermediateProfessional Cloud Architect
Cloud Identity SAML Federation with Microsoft Entra ID
Integrating solutions with existing systems
AdvancedProfessional Cloud Security Engineer
FIDO2 Security Key Enforcement
Configuring and enforcing 2-step verification.
Last updated