Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Cloud DNS Failover Routing for Regional Outages
Free sample question, answered and explained below. The Professional Cloud Architect practice bank has 2,335 more like it. Try 10 free: instant score, no account.
An organization is architecting a multi-region disaster recovery strategy for an externally accessible, mission-critical web application on Google Cloud. The architecture must satisfy the following business continuity requirements:
- The primary deployment runs behind an external Application Load Balancer in the
us-east4region. - A standby deployment runs behind a redundant external Application Load Balancer in the
us-central1region. - Client traffic must fail over automatically to the secondary region when the primary region experiences an outage and automatically fail back when it recovers.
- Downtime during a regional outage must be minimized through fast DNS resolution updates.
How should you configure Cloud DNS and health checking to achieve automated cross-region failover and failback?
Explanations
Create a global health check configured with three source regions targeting the primary forwarding rule IP address, configure a Cloud DNS record set with a Failover routing policy referencing the health check, and set the record TTL to 30–60 seconds.
Create a global health check configured with three source regions targeting the primary forwarding rule IP address, configure a Cloud DNS record set with a Failover routing policy referencing the health check, and set the record TTL to 30–60 seconds.
What this solution is
This solution implements automated cross-region failover and failback by pairing Cloud DNS Failover routing policies with Google Cloud distributed health checks targeting regional external Application Load Balancer forwarding rules.
How it meets the requirements
- Automated failover and failback: Cloud DNS monitors the health of the primary regional forwarding rule IP address using distributed probers across three specified source regions. When the primary forwarding rule fails the configured unhealthy threshold, Cloud DNS automatically steers DNS queries to the backup forwarding rule. When the primary region recovers and health check probes succeed, Cloud DNS automatically fails back traffic.
- Minimized RTO and downtime: Outage duration is governed by the formula
DNS TTL + (Health Check Interval * Unhealthy Threshold). Setting the DNS record TTL to 30–60 seconds ensures client caches expire rapidly, redirecting user traffic to the healthy secondary region with minimal delay.
Cloud DNS Failover Across Regional Load Balancers
System Architecture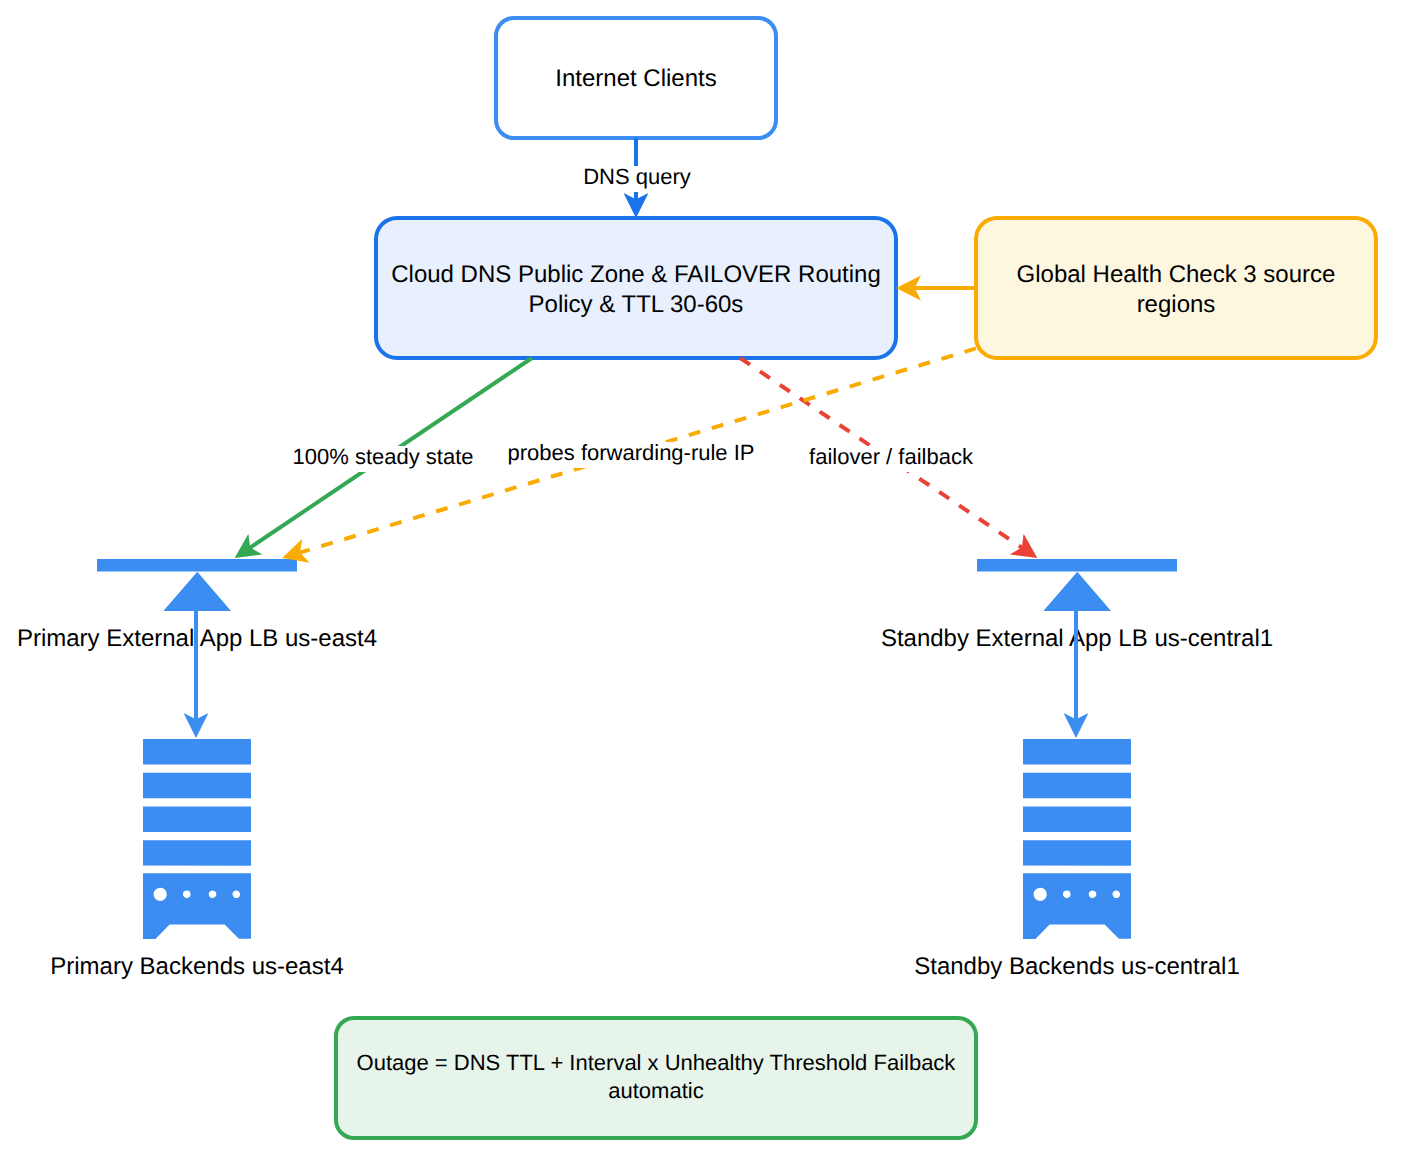
Key advantages
- Resilience to regional failures: Cloud DNS is a globally distributed, Anycast-routed service capable of serving DNS answers even if an entire cloud region suffers an outage.
- Standardized health probing: Requiring exactly three source regions prevents false-positive failovers caused by localized network partitions.
- Zero manual intervention: Traffic redirection on failure and restoration during recovery occur automatically without operator overhead.
Why this is optimal
This approach aligns with Google Cloud architectural best practices for cross-region disaster recovery, balancing swift failure detection against protection against transient flap errors.
Create an external passthrough Network Load Balancer in each region, set the failover ratio to 0.0, and configure Cloud DNS to use weighted round-robin routing.
Create an external passthrough Network Load Balancer in each region, set the failover ratio to 0.0, and configure Cloud DNS to use weighted round-robin routing.
What this option is/does
This configuration deploys Network Load Balancers (Layer 4 passthrough) with a failover ratio of 0.0 and uses Cloud DNS Weighted Round Robin (WRR) routing policies.
Why it doesn't meet the requirement
- Incorrect load balancer tier: Passthrough Network Load Balancers operate at Layer 4 (TCP/UDP) and do not provide Layer 7 Application Load Balancing features like host/path routing and SSL certificate termination.
- No automated health-based failover: Weighted Round Robin distributes traffic based on static percentage weights rather than dynamic health status. If a region goes down, weighted records continue sending traffic to the failed IP unless manually modified.
- Misconfigured failover ratio: A failover ratio of
0.0means failover to backup pools would never trigger based on primary backend health thresholds.
Key limitations
- WRR routing policies lack health-checking integration for primary/standby disaster recovery.
- Layer 4 load balancers cannot inspect HTTP/HTTPS application health metrics.
This answer would be correct if
You wanted to split static percentages of TCP traffic across multiple functioning regions for canary testing.
Deploy a Cloud Service Mesh service load balancing policy with the spray-to-world algorithm, and configure Cloud DNS with a Geo routing policy with a 3600-second TTL.
Deploy a Cloud Service Mesh service load balancing policy with the spray-to-world algorithm, and configure Cloud DNS with a Geo routing policy with a 3600-second TTL.
What this option is/does
This option applies a Cloud Service Mesh service load balancing policy using the spray-to-world algorithm across client proxies, combined with a Geo routing policy in Cloud DNS with a 1-hour (3600 seconds) TTL.
Why it doesn't meet the requirement
- Wrong use case: Cloud Service Mesh controls east-west traffic between internal microservices using Envoy sidecars, rather than managing ingress failover for external web traffic.
- Increased cross-region latency: The
spray-to-worldalgorithm spreads client requests globally across all instances in all regions simultaneously, defeating active-standby isolation and increasing network transit costs. - Severe failover delay: A 3600-second TTL (1 hour) violates the minimal downtime requirement, keeping clients pinned to an unavailable IP address long after an outage begins.
Key limitations
- Spray-to-world does not provide primary/standby disaster recovery failover semantics.
- Long TTLs prevent rapid DNS switching during disaster events.
This answer would be correct if
You were configuring internal service-to-service mesh communication that required uniform request distribution across all global backends.
Configure a single regional health check in us-east4, attach it directly to the Cloud DNS managed zone, and configure an A record with a 300-second TTL pointing to both forwarding rule IP addresses.
Configure a single regional health check in us-east4, attach it directly to the Cloud DNS managed zone, and configure an A record with a 300-second TTL pointing to both forwarding rule IP addresses.
What this option is/does
This option attempts to monitor the primary load balancer using a regional health check located inside us-east4 and points a standard multi-value A record with a 5-minute (300 seconds) TTL to both load balancers.
Why it doesn't meet the requirement
- Fate sharing during outages: A health check hosted solely within the failing region (
us-east4) may become unreachable or fail to report status, preventing reliable failover coordination. - No automated routing policy: A standard multi-value A record performs basic round-robin DNS resolution across both IPs rather than active-passive failover, causing 50% of client traffic to hit the dead region during an outage.
- Excessive RTO: A 300-second TTL delays failover significantly because client resolvers cache the failed endpoint for 5 minutes.
Key limitations
- Regional health checks cannot be used by Cloud DNS routing policies for external load balancer endpoints.
- Lacks the necessary failover and backup data structures in Cloud DNS.
This answer would be correct if
You needed simple round-robin DNS load balancing without automated health-checking failover controls.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,335 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
IntermediateProfessional Cloud Architect
Warm Standby Disaster Recovery Pattern
Business continuity plan
IntermediateProfessional Cloud Architect
Cloud SQL Advanced Disaster Recovery
Business continuity plan
IntermediateProfessional Cloud Architect
Partner Interconnect vs Dedicated Interconnect
Integration patterns with external systems
IntermediateProfessional Cloud Architect
SLIs and SLOs for Critical User Journeys
Success measurements (e.g., key performance indicators [KPI], return on investment [ROI], and metrics)
IntermediateProfessional Cloud Architect
Cloud Emulator IAM and Performance Limitations
Cloud Emulators (e.g., Bigtable, Spanner, Pub/Sub, and Firestore)
AdvancedProfessional Cloud DevOps Engineer
Config Sync RootSync vs RepoSync
Managing Google Kubernetes Engine (GKE) clusters across an enterprise (e.g., fleets)
Last updated