Fundamental
Prepare and test your skills
Fundamental
Prepare and test your skills
Uniform Bucket-Level Access Enforces IAM-Only Control
Free sample question, answered and explained below. The Associate Data Practitioner practice bank has 1,156 more like it. Try 10 free: instant score, no account.
A data engineering team is setting up Cloud Storage buckets to host raw and processed datasets. The security team requires a centralized, simplified security model that prevents individual object-level Access Control Lists (ACLs) from overriding organizational policies, ensuring that permissions are governed exclusively through hierarchical Identity and Access Management (IAM) roles.
Which Cloud Storage access control configuration should the team implement to satisfy these security requirements?
Explanations
Grant the Storage Object Viewer role at the organization level and configure object-level ACLs for all write operations.
Grant the Storage Object Viewer role at the organization level and configure object-level ACLs for all write operations.
What this option describes
This option proposes granting broad read access (roles/storage.objectViewer) across the entire organization hierarchy while delegating write permissions to individual object-level Access Control Lists (ACLs).
Why it doesn't meet the requirement
- Violates least privilege: Granting the Storage Object Viewer role at the organization root allows all principals with that role to view every Cloud Storage object across every project in the entire organization.
- Splits permission systems: Dividing read permissions into IAM and write permissions into ACLs makes security audits fragmented and error-prone.
- Fails the uniform management requirement: It continues relying on object ACLs rather than enforcing a centralized, IAM-only security architecture.
Key characteristics and limitations
- Broad inheritance: Hierarchical IAM roles granted at the organization level propagate automatically down to all folders, projects, and buckets.
- Inconsistent governance: Using ACLs for write operations prevents security teams from enforcing uniform write policies via IAM conditions or group memberships.
- Operational friction: Developers must explicitly configure ACL parameters during every object write call.
This answer would be correct if
The organization intended for all data across every bucket to be globally readable by all employees, while requiring individual object uploaders to manually specify writers per file.
Assign the Storage Object Admin role directly to individual objects while maintaining active bucket ACLs.
Assign the Storage Object Admin role directly to individual objects while maintaining active bucket ACLs.
What this option describes
This option suggests granting the Storage Object Admin (roles/storage.objectAdmin) IAM role directly at the individual object level while keeping ACLs enabled on the bucket.
Why it doesn't meet the requirement
- Incorrect IAM abstraction: Standard IAM roles in Cloud Storage are assigned at the project, folder, organization, or bucket level (or via Managed Folders), not directly on arbitrary individual object instances in standard bucket layouts.
- Retains active ACLs: Keeping ACLs active does not achieve the requirement to disable ACLs and simplify security operations exclusively through IAM.
- High administrative overhead: Attempting to manage permissions object-by-object contradicts the goal of centralized, hierarchical access management.
Key characteristics and limitations
- Standard IAM scope: Standard Cloud Storage IAM policies are bound to buckets or higher container levels in the resource hierarchy.
- Dual-layer risk: Leaving ACLs active allows object uploaders to inadvertently expose individual files via ACL settings.
- Administrative burden: Managing permissions per object creates severe scalability bottlenecks as bucket contents grow to millions of files.
This answer would be correct if
A user needed full administrative permissions over all objects within a specific bucket or project, where granting roles/storage.objectAdmin at the bucket or project level would be appropriate.
Enable Uniform Bucket-Level Access on the buckets to disable ACLs and manage all permissions exclusively through IAM.
Enable Uniform Bucket-Level Access on the buckets to disable ACLs and manage all permissions exclusively through IAM.
What Uniform Bucket-Level Access is
Uniform Bucket-Level Access is a Cloud Storage security feature that unifies and simplifies access management by disabling Access Control Lists (ACLs) for a bucket and all of its contained objects. When enabled, access to objects is evaluated strictly through Identity and Access Management (IAM) policies defined at the bucket level or inherited from higher levels in the resource hierarchy.
How it meets the requirements
- Exclusively relies on IAM: Enabling Uniform Bucket-Level Access completely deactivates ACL evaluation, preventing object-level permissions from being assigned or modified independently.
- Enforces hierarchical governance: IAM permissions assigned at parent resource levels (such as Organizations, Folders, or Projects) or directly at the Bucket level apply consistently to all objects inside the bucket.
- Prevents permission drift: Object uploaders cannot grant unauthorized third-party read/write permissions via object ACLs, eliminating inconsistent security configurations across individual files.
IAM Inheritance from Org to Objects
Hierarchy / Taxonomy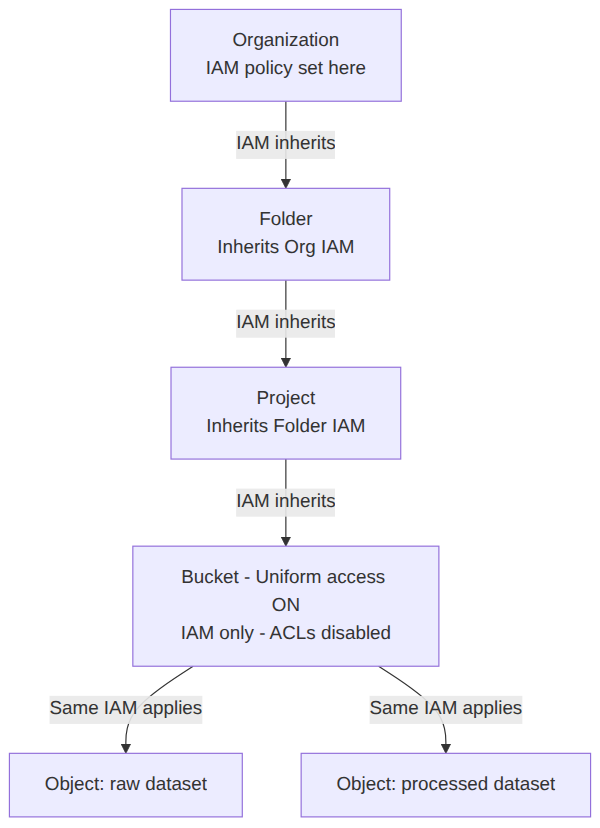
Key advantages and capabilities
- Consistent permission model: Aligns Cloud Storage with the standard Google Cloud IAM model used across other services like BigQuery and Compute Engine.
- Simplified auditing and compliance: Security administrators can audit access by inspecting bucket and project IAM policies rather than parsing ACLs across millions of distinct objects.
- Integration with advanced security features: Enables support for IAM Conditions, VPC Service Controls, and Organization Policies that enforce uniform access across all organization buckets.
- Reduced administrative overhead: Eliminates the need to maintain, inspect, and update object-level access metadata.
Why this is optimal
Uniform Bucket-Level Access is the Google Cloud recommended best practice for securing data buckets. It removes the dual-system complexity of managing both IAM policies and legacy ACLs simultaneously, ensuring that all access decisions follow centralized, hierarchical governance.
Configure fine-grained access control on the buckets to allow object ACLs to override project-level IAM policies.
Configure fine-grained access control on the buckets to allow object ACLs to override project-level IAM policies.
What fine-grained access control is
Fine-grained access control is the dual-system access model in Cloud Storage where both IAM policies and Access Control Lists (ACLs) are evaluated concurrently. In this mode, ACLs can be attached directly to individual objects to provide object-specific permissions.
Why it doesn't meet the requirement
- Does not simplify governance: Fine-grained access requires security teams to monitor both bucket-level IAM policies and individual object ACLs, significantly increasing management complexity.
- Allows object-level ACL overrides: Individual object ACLs can grant access to users who lack bucket-level IAM permissions, undermining centralized access controls.
- Fails the exclusivity requirement: The scenario requires managing permissions exclusively through IAM and eliminating object ACLs.
Key characteristics and limitations
- Dual-evaluation model: Access is granted if either IAM OR the object ACL permits the action.
- Audit complexity: Auditing access requires inspecting metadata across every single object in the bucket rather than checking a single IAM policy.
- Legacy mechanism: Fine-grained access with ACLs is primarily retained for backward compatibility with systems relying on Amazon S3-style ACL architectures.
This answer would be correct if
The scenario required granting distinct, highly customized read or write access to specific files within the same bucket to different users without creating separate buckets.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 1,156 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Data Practitioner
Uniform Bucket-Level Access
Compare methods of access control for Cloud Storage (e.g., public or private access, uniform access)
FundamentalAssociate Data Practitioner
Uniform Bucket-Level Access
Compare methods of access control for Cloud Storage (e.g., public or private access, uniform access)
FundamentalAssociate Data Practitioner
Storage Transfer Service Synchronization Options
Load data into Google Cloud storage systems using the appropriate tool (e.g., gcloud and BQ CLI, Storage Transfer Service, BigQuery Data Transfer Service, client libraries)
FundamentalAssociate Data Practitioner
Cloud Storage Location Type Selection
Choose the appropriate data storage location type (e.g., regional, dual-regional, multi-regional, zonal)
FundamentalAssociate Data Practitioner
Cloud SQL Cross-Region Read Replica
Determine when to use replication
FundamentalGenerative AI Leader
Vertex AI Imagen Text-to-Image
Imagen
Last updated