Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Overriding External IP Deny Policy in Folders
Free sample question with answers and detailed explanation below. The Associate Cloud Engineer practice bank has an additional 2,014 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
Your company enforces an organization policy at the root organization node that restricts external IP addresses on Compute Engine instances by applying the constraints/compute.vmExternalIpAccess list constraint set to Deny All.
A team in the Development folder needs to assign external IP addresses to test virtual machines (VMs) for an external payment gateway integration. The rest of the organization must continue to block external IP access.
What should you do to meet this requirement?
Explanations
Grant the Compute Admin role (roles/compute.admin) to the development team on the Development folder to bypass organization policies
Grant the Compute Admin role (roles/compute.admin) to the development team on the Development folder to bypass organization policies
What the Compute Admin Role Does
The Compute Admin (roles/compute.admin) role provides full control over Google Compute Engine resources, such as creating, modifying, and deleting virtual machines, disks, networks, and firewalls.
Why It Doesn't Meet the Requirement
- Cannot Bypass Policies: Identity and Access Management (IAM) permissions and Organization Policies are separate, complementary security layers. IAM controls who can perform actions, whereas Organization Policies define what configurations are allowed on resources.
- Enforcement Priority: Even a principal with full administrative rights (such as
roles/compute.adminorroles/owner) cannot violate an active Organization Policy constraint. Attempting to attach an external IP address while the constraint is active will return an authorization failure regardless of IAM privileges.
Key Characteristics and Limitations
- IAM Scope: Authorizes API method calls (e.g.,
compute.instances.create), but does not evaluate resource configuration guardrails. - Separation of Duties: Keeps resource creation permissions distinct from security governance.
- Privilege Escalation Risk: Granting broad admin roles without resolving the policy constraint increases administrative risk without solving the technical restriction.
This Answer Would Be Correct If
The development team already had a policy override in place allowing external IPs, but was receiving an HTTP 403 Forbidden error due to lacking the underlying IAM permission to create and configure Compute Engine network interfaces.
Set an organization policy on the Development folder for constraints/compute.vmExternalIpAccess, select the option to override the parent policy, and set the rule to Allow All
Set an organization policy on the Development folder for constraints/compute.vmExternalIpAccess, select the option to override the parent policy, and set the rule to Allow All
What Organization Policy Overrides Are
Organization Policy hierarchy inheritance in Google Cloud allows administrators to set guardrails globally at the organization level while overriding or modifying those rules on specific folders or projects. By default, child resources inherit policies from their parent resource, but an administrator with the Organization Policy Administrator (roles/orgpolicy.policyAdmin) role can explicitly override inheritance at lower levels of the resource hierarchy.
How It Meets the Requirement
- Folder-level Exception: By applying a policy directly to the
Developmentfolder, you target only the resources within that specific boundary. - Override Parent Policy: Selecting Override parent policy (or replacing policy inheritance) decouples the
Developmentfolder from the root organization's Deny All rule forconstraints/compute.vmExternalIpAccess. - Preserve Global Security: The root organization policy remains strictly enforced across all other folders and projects, ensuring that production and corporate environments continue to disallow external IP addresses.
Contained Exception Keeps Org Secure
Decision Tree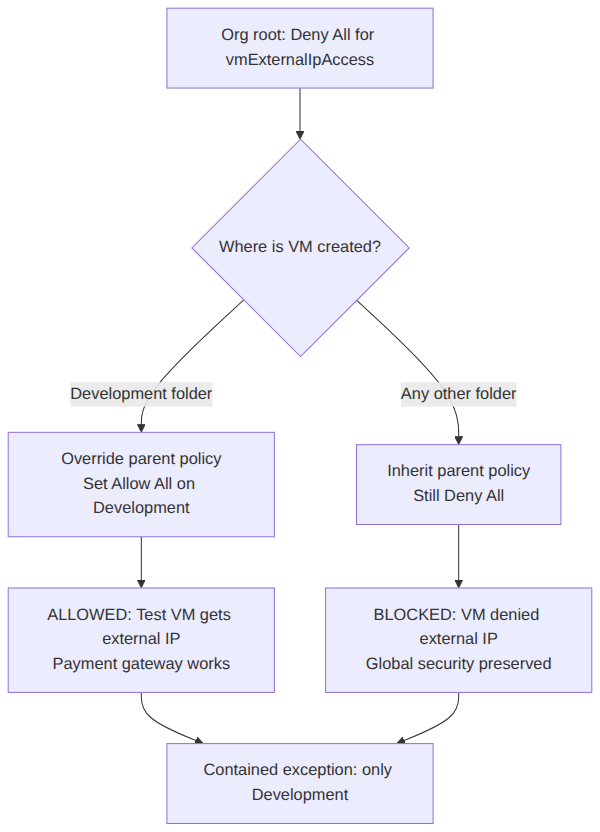
Key Advantages and Capabilities
- Granular Governance: Enables tailored policy configurations that balance enterprise security guardrails with developer flexibility.
- Inheritance Control: Child nodes can inherit, append to, or completely replace policy rules defined by parent resource containers.
- Automated Enforcement: Once set at the folder level, any new projects or VMs created inside the
Developmentfolder automatically receive the override without manual intervention. - Auditing and Compliance: Changes to policy constraints are fully logged in Cloud Audit Logs, maintaining traceability across the hierarchy.
Why This Is Optimal
This approach follows Google Cloud best practices by managing policy exceptions natively through the resource hierarchy rather than modifying IAM roles or dismantling top-level controls.
Disable the Organization Policy Service API (orgpolicy.googleapis.com) in all projects located in the Development folder
Disable the Organization Policy Service API (orgpolicy.googleapis.com) in all projects located in the Development folder
What Disabling the Organization Policy Service API Does
The Organization Policy Service API (orgpolicy.googleapis.com) is the control-plane API used to manage, view, and modify organization policies across the Google Cloud resource hierarchy.
Why It Doesn't Meet the Requirement
- Policies Remain Active: Disabling the API inside a child project only prevents programmatic management calls (such as
gcloud org-policies create) from interacting with the service within that project; it does not stop policy enforcement. - Control Plane vs. Data Plane: Organization policy constraints are evaluated automatically by Google Cloud backend service controllers (like Compute Engine) at resource creation time, not via client API calls in the target project.
- No Functional Relief: VMs created in those projects would still be evaluated against the inherited root policy and denied external IP allocation.
Key Characteristics and Limitations
- Service Enforcement: Resource restrictions are built into the resource managers of individual GCP services.
- API Scope: Service APIs enable management endpoints, but core platform security constraints cannot be disabled by deactivating local project APIs.
- Management Disruption: Disabling the API hinders administrators from inspecting or troubleshooting applied policies via the CLI or Console.
This Answer Would Be Correct If
You wanted to prevent automation scripts running inside a project from querying or listing the organization policy configuration metadata via API endpoints.
Delete the organization policy at the organization root node and re-create it on every folder except the Development folder
Delete the organization policy at the organization root node and re-create it on every folder except the Development folder
What Deleting Root Policies and Re-creating Them Does
This approach removes top-level governance at the organization node and attempts to maintain policy coverage by manually attaching identical organization policy constraints to every non-development folder individually.
Why It Doesn't Meet the Requirement
- High Administrative Overhead: Managing policies individually on dozens or hundreds of folders is tedious, error-prone, and contrary to recommended architectural practices.
- Security Blind Spots: Any newly created folder or project placed at the organization root will have no policy applied by default, exposing the organization to security non-compliance.
- Violates Hierarchy Principles: Google Cloud provides built-in policy override mechanisms specifically designed to avoid removing global root policies.
Key Characteristics and Limitations
- Scalability Issues: Does not scale in enterprise environments with evolving resource hierarchies.
- Risk of Drift: Inconsistent configuration across folders can quickly lead to configuration drift and audit compliance failures.
- Manual Maintenance: Requires continuous updates whenever teams add new folders or reorganize resources.
This Answer Would Be Correct If
The organization policy framework did not support hierarchical inheritance or overrides, making manual per-container policy assignment the only available configuration method.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 2,014 practice questions across all 4 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalAssociate Cloud Engineer
Organization Policy Inheritance
Applying organizational policies to the resource hierarchy
FundamentalAssociate Cloud Engineer
Organization Policy List vs Boolean Constraints
Applying organizational policies to the resource hierarchy
FundamentalAssociate Cloud Engineer
Cloud Logging Bucket Log Analytics Upgrade
Configuring log buckets, log analytics, and log routers
FundamentalAssociate Cloud Engineer
gcloud spanner databases execute-sql
Executing queries to retrieve data from data instances (e.g., Cloud SQL, BigQuery, Bigtable, Spanner, Firestore, AlloyDB)
FundamentalAssociate Cloud Engineer
Cloud SQL Query Insights Index Advisor
Using cloud diagnostics to research an application issue (e.g., Cloud Trace, Cloud Profiler, Query Insights, index advisor)
FundamentalCloud Digital Leader
LookML Semantic Modeling Layer
Describe how Looker democratizes access to data by empowering individuals to self-serve business intelligence and create insights.
Last updated