Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Hybrid Integration with On-Premises and Multi-Cloud
Application and data interoperability patterns are reusable designs that let new Google Cloud applications exchange requests and data with existing on-premises and multi-cloud systems. The patterns use Apigee (opens in a new tab) as the central API platform, Private Service Connect (opens in a new tab) for private network paths, and small local gateways for legacy backends. Together they control where traffic enters, how it is secured and observed, and how workloads can move in phases without disrupting business operations.
Gated Ingress with Apigee as the API Platform
Gated ingress with Apigee as the API platform is a design where all inbound API calls must pass through a managed gateway before reaching a backend. Apigee provides controlled entry with built-in gateway behavior for fronting backend APIs, security for authentication and policy enforcement, rate limiting to protect backends from overload, and analytics for visibility into API use. This central control point lets teams enforce consistent policy even when backends live in different environments.
Traffic in the gated ingress path flows in a fixed order from the remote environment to the application. Traffic flows from on-premises or another cloud over Cloud VPN or Cloud Interconnect to a Private Service Connect endpoint in the application Virtual Private Cloud (VPC) that is associated with the Apigee VPC. Traffic then flows from that endpoint to an internal load balancer in the application VPC, and the load balancer forwards the request to the application APIs. Firewall rules and traffic filtering in the application VPC provide fine-grained access control, and restricting advertisement of the backend subnet to the on-premises network prevents clients from bypassing the Private Service Connect endpoint and gateway.
When inspection outside the application VPC is required, the design adds a separate transit VPC between hybrid connectivity and the application VPC. In that path, traffic flows from the remote environment through the transit VPC to the Private Service Connect endpoint, where next generation firewalls as network virtual appliances or Cloud Next Generation Firewall Enterprise with intrusion prevention service perform deep packet inspection. The inspected traffic then continues to the internal load balancer and application in the application VPC. Multiple Private Service Connect endpoints can exist in the same VPC network, with Cloud Router and VPC firewall rules selecting different paths and with Private Service Connect global access providing failover options.
Apigee Adapter for Envoy for Remote and Legacy Backends
Apigee Adapter for Envoy (opens in a new tab) is a small-footprint, Apigee-managed gateway that runs close to backend applications on premises or in another cloud. The adapter avoids deploying a full Apigee installation in every data center, which would be large and complex because of data-heavy features such as key management, monetization, and analytics. The adapter instead splits responsibilities between a management plane on Google Cloud and a data plane that runs remotely with the Envoy proxy and the Apigee Remote Service.
A client request moves through the adapter data plane in a fixed order:
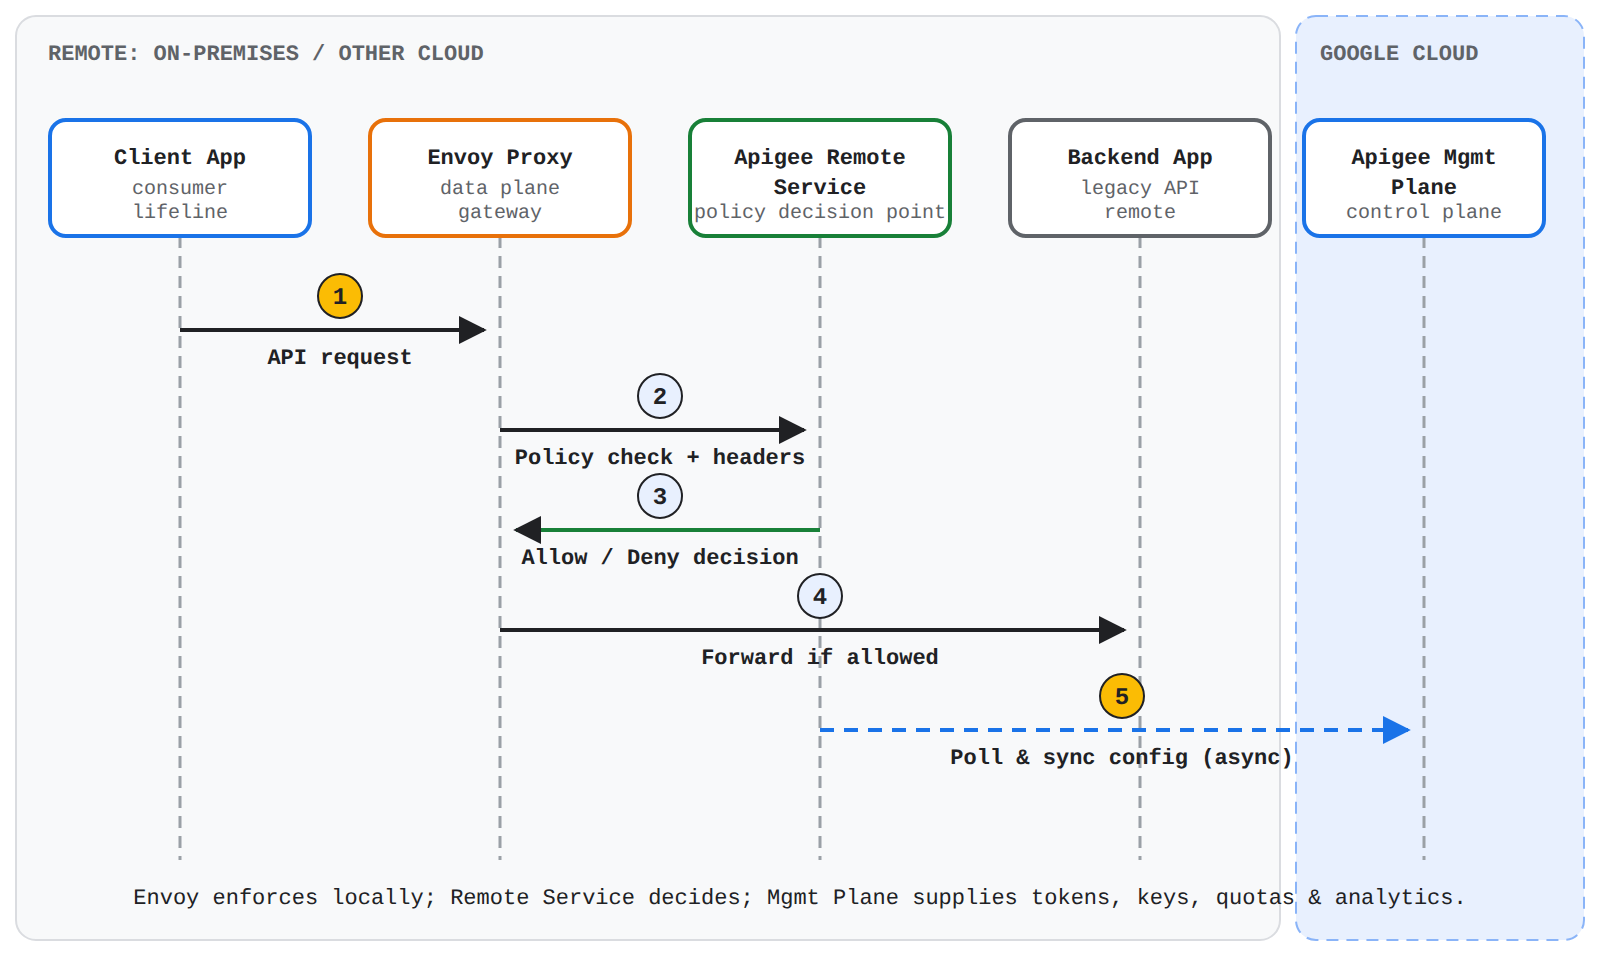
A sequence diagram with five lifelines showing the Apigee Adapter for Envoy flow: client to Envoy, policy check to Remote Service, allow decision back, forward to backend, and async config sync to Google Cloud.
- Client access: A consumer or client app accesses an API endpoint exposed by the Envoy proxy.
- Policy check: The Envoy proxy passes the security context in HTTP headers to the Apigee Remote Service, which acts as a policy decision point and advises Envoy to allow or deny the request.
- Forwarding: If the call is allowed, the Envoy proxy forwards the request to the backend application.
- Configuration sync: The Apigee Remote Service asynchronously polls the Apigee management plane and downloads the proxy, API product, and other configuration it needs to operate.
Running the gateway near the backend provides consistent API management during phased migration with reduced latency for nearby services, use of the full suite of Apigee analytics metrics and dashboards, API traffic staying within enterprise-approved boundaries, and asynchronous communication that captures traffic data without adding latency. The adapter still depends on the Apigee management plane for control functions even though API traffic stays local:
- Generating OAuth tokens for authentication flows
- Verifying API keys, where the first verification requires a connection and later checks use a cache
- Enforcing quotas on API use
- Sending analytics data to the management plane
Exam tip: The adapter tolerates temporary loss of connectivity to the management plane, but API key verification requires a connection for the first check and OAuth token generation always requires connectivity.
Bidirectional Integration with Private Service Connect
Bidirectional integration with Private Service Connect lets applications in different environments call each other as private APIs without using the public internet or overlapping IP addresses. One direction uses a Private Service Connect endpoint to expose a service in a producer VPC to a consumer VPC, and that connectivity can extend over hybrid connectivity to on-premises or another cloud. The two connectivity paths in this design are independent connections for different purposes, not two directions of a single connection.
A Private Service Connect endpoint handles the client-to-service direction, while a Private Service Connect interface handles the reverse direction where the hosted service needs to reach back. A Private Service Connect interface is a network interface attached to the consumer or transit VPC that is shared with a producer virtual machine (VM) instance while keeping producer and consumer roles separate. With that interface, the application VM in the producer VPC can access consumer resources as if they resided locally, including external destinations reachable from the consumer VPC over hybrid connectivity such as an on-premises data source.
| Option | Direction of access | Purpose |
|---|---|---|
| Private Service Connect endpoint | Traffic flows from consumer VPC to a service published in the producer VPC | Expose Google APIs such as Cloud Storage or BigQuery, or expose an application backend, as a private address to remote environments |
| Private Service Connect interface | Traffic flows from a producer VM instance into the consumer VPC and beyond | Let a Google Cloud application retrieve data from sources in the consumer VPC or from on-premises networks reachable through that VPC |
When the consumer VPC belongs to an external organization, the producer often cannot control security in the consumer VPC. In that case, security policies must be defined in the guest operating system of the Private Service Connect interface VM, or an alternative approach must be chosen if that control does not meet compliance requirements.
Planning Traffic Paths and Protecting Data Flow
Planning hybrid API paths is the process of identifying which traffic must go to a local gateway versus a remote gateway, including the source and destination environments. Client requests arrive at the application frontend directly in the environment that hosts the application, while Apigee in Google Cloud exposes Google Cloud-hosted frontends or backends and Apigee hybrid exposes frontends or backends hosted in the other environment. A transit VPC can separate hybrid connectivity and security inspection from the application VPC, and direct VPC peering with route exchange or a Private Service Connect endpoint linked to a load balancer with a hybrid endpoint group backend can carry application-initiated requests through the transit VPC.
Protection for these paths combines network controls and service perimeters to preserve operational continuity. VPC Service Controls protects Google Cloud services by defining service perimeters at the project or VPC network level to reduce data exfiltration risk, and those perimeters can extend to a hybrid environment over an authorized VPN or Cloud Interconnect. VPC firewall rules or firewall policies control network-level access to Private Service Connect resources, such as outbound rules in the consumer VPC that restrict which VM instances can reach an endpoint IP address or subnet. For sustained high-volume outbound transfers in long-term hybrid or multi-cloud setups, use Cloud Interconnect or Cross-Cloud Interconnect and terminate user connections at the frontend in the appropriate environment with Apigee hybrid to reduce latency and cost.
Hybrid and multicloud connectivity is the set of connections that link on-premises networks, Google Cloud, and other clouds. These connections carry all traffic between environments, so bandwidth, latency, packet loss, and jitter directly affect application performance. Choosing a connectivity product means weighing service-level agreements (SLAs), performance, security, cost, reliability, and bandwidth together rather than in isolation.
Choosing a Connectivity Option
Choosing a connectivity option starts with matching business and application requirements to transport type, cost, and throughput. Cloud VPN (opens in a new tab) networks and Compute Engine instances can be reached over the internet with public IP addresses, over APIs with Transport Layer Security encryption, over private IP addresses with VPN, or over private transport with interconnect. For long-term setups with high outbound volume, private interconnect options can improve performance and may reduce outbound data transfer charges when traffic meets pricing conditions.
The following table compares the main hybrid transports and when to choose each:
| Option | Transport | Choose when |
|---|---|---|
| Cloud VPN | IPsec VPN over the public internet | Lower cost, lower bandwidth needs, experimenting with migration, or occasional low-volume exchange |
| Partner Interconnect | Private transport through a service provider | Larger data transfers with dedicated capacity, normally less than 10 Gbps per connection, without managing colocation hardware |
| Dedicated Interconnect (opens in a new tab) | Private direct connection in a colocation facility | Typical transfer rates of 10 Gbps or more and the team can manage routers, cross-connects, and a common point of presence |
| Cross-Cloud Interconnect (opens in a new tab) | Private managed connection between clouds | Connecting Google Cloud to another cloud provider without managing cross-connects and routing equipment in remote locations |
Use Cloud Interconnect instead of Direct Peering, Carrier Peering, or Verified Peering Provider when connecting to Google Cloud resources, unless access to Google Workspace applications requires peering. Network Connectivity Center can orchestrate connectivity when many VPC networks, router appliances, or hybrid connections must connect through a central hub with route exchange to Cloud Router.
Cloud VPN and HA VPN Solutions
Cloud VPN provides private, secure connectivity over the public internet using IPsec encryption, including customer-managed VPN gateways and partner network virtual appliances such as software-defined WAN. High-availability (HA) VPN is the high-availability Cloud VPN solution that securely connects an on-premises network to a VPC network through IPsec VPN tunnels. Based on topology and configuration, HA VPN can provide 99.99% or 99.9% service availability.
An HA VPN gateway automatically receives two external IP addresses, one for each interface from a unique address pool, and each interface supports multiple tunnels. Traffic flows from the on-premises peer VPN gateway, which is represented in Google Cloud by an external VPN gateway resource, to the HA VPN gateway interfaces and then into the VPC network. A gateway configured with only one active interface and one external IP address does not provide an availability SLA. When more volume is needed than a single tunnel supports, the active/active HA VPN routing option increases throughput and resilience.
Cloud Interconnect with Dedicated, Partner, and Cross-Cloud Options
Cloud Interconnect provides private connectivity over private transport with more deterministic performance and an SLA, in three forms: Dedicated Interconnect, Partner Interconnect, and Cross-Cloud Interconnect. Dedicated Interconnect is a direct dedicated connection ordered in a colocation facility, while Partner Interconnect connects a VPC network through a supported service provider. When choosing between them, consider connection location and required capacity.
Dedicated Interconnect through a common point of presence requires hosting and maintaining physical routers where Google Cloud and the other environment are both present. Routes are exchanged between Cloud Router (opens in a new tab) and the other side through Border Gateway Protocol on that router, and traffic flows through the router between environments. Partner Interconnect avoids managing that hardware but involves three availabilities: Google, the interconnect partner, and the other cloud provider. Redundant Partner Interconnect offers 99.9% to 99.99% monthly SLA depending on topology, while a single Partner Interconnect connection has no SLA. Cross-Cloud Interconnect offers managed private connectivity between Google Cloud and supported providers with high-availability options of 99.9% and 99.99%, which lowers total cost by removing cross-connect management.
Encryption in Transit and Private Access
Encryption behavior differs between VPN and interconnect transports. Cloud VPN encrypts traffic between environments at the connectivity layer by default. Cloud Interconnect does not encrypt by default, so use HA VPN over Cloud Interconnect for IPsec encryption with interconnect capacity, or Media Access Control Security (MACsec) for Cloud Interconnect for network-layer encryption. With HA VPN over Cloud Interconnect, traffic never traverses the public internet, and HA VPN gateways associated with virtual local area network attachments can use regional internal IP addresses.
Cloud Router uses Border Gateway Protocol to provide dynamic routing for Cloud VPN gateways and Cloud Interconnect attachments. Private Service Connect lets workloads in Google Cloud, on-premises, or another cloud with hybrid connectivity privately access Google APIs or published services using internal IP addresses. When using Private Service Connect, control who can deploy Private Service Connect resources, whether connections can be established between consumers and producers, and which network traffic is allowed to access those connections.
Exam tip: Cloud VPN encrypts traffic by default, while Cloud Interconnect requires HA VPN over Cloud Interconnect or MACsec for encryption at the connectivity layer.
Hybrid DNS Integration
Hybrid DNS integration keeps two authoritative systems: Cloud DNS for private Google Cloud names and existing on-premises DNS servers for on-premises names. Designate a single VPC network to forward queries to on-premises name servers with outbound forwarding, then let additional VPC networks target that designated VPC network with a DNS peering zone. This avoids the limit where a peered VPC network cannot use another VPC network's peering connection to reach on-premises DNS.
VPC Network Peering and DNS peering are different mechanisms with different trust boundaries. VPC Network Peering allows VM instances in multiple projects to reach each other, but each VPC network still follows its own name resolution order. DNS peering unidirectionally forwards DNS requests for specific zones from a consumer VPC network to a producer VPC network and does not require a bidirectional peering relationship. Common reference patterns are a single Shared VPC network connected on-premises, multiple separate VPC networks sharing the same on-premises DNS, and a hub VPC network peered to multiple spoke VPC networks.
Shared VPC, Addressing, and Monitoring
Shared VPC lets multiple projects share a common VPC network instead of creating many separate VPC networks, when that matches the resource hierarchy design. In a hub-and-spoke variation, development and test VPC networks connect to a central hub VPC that holds common services such as monitoring, configuration management, continuous integration and continuous delivery, and authentication. All inter-VPC and hybrid connectivity passes through the hub VPC, where communication can be controlled centrally.
Allow enough existing RFC 1918 private address space to accommodate cloud-hosted systems. If an IP range must be kept during migration, use hybrid subnets to reuse the same internal addresses on-premises and in Google Cloud, or use bring your own IP to provision owned public IPv4 addresses for Google Cloud resources. Network Intelligence Center provides a single console for network visibility, monitoring, and troubleshooting to maintain reliable hybrid communication.
Identity federation and access management is the design that lets employees use one existing corporate identity to sign in to Google Cloud while Cloud Identity (opens in a new tab) centralizes provisioning and access control. Federation has two linked parts: user and group accounts are provisioned from an external authoritative source into Cloud Identity or Google Workspace, and authentication is delegated to an external identity provider through Single Sign-On. This combination keeps security policy consistent across on-premises, Google Cloud, and multi-cloud environments without synchronizing passwords to Google.
Unified Identity Framework with Cloud Identity
A unified identity framework separates the authoritative source for identities from the identity provider used for authentication. The authoritative source is the single system that creates, manages, and deletes employee identities, such as Active Directory, Microsoft Entra ID, an identity as a service product like Okta, or a human resources information system. The identity provider is the single system that verifies credentials and issues SSO assertions, while Cloud Identity holds a matching user whose primary email address defines the Google identity. Because Google Sign-In matches the NameID claim in the SAML assertion to that primary email address, using the same email-based identity in both systems avoids confusing double prompts and mapping errors.
Synchronizing Directory Services with Cloud Identity
Synchronizing directory services is the one-way provisioning of users and groups from the corporate directory into Cloud Identity or Google Workspace so the external directory remains the source of truth. Google Cloud Directory Sync (opens in a new tab) is the free Google-provided tool that syncs users and groups from Active Directory, and Entra ID and identity as a service products provide automatic provisioning to Cloud Identity through their publicly accessible APIs. Because the Cloud Identity API is publicly accessible, this synchronization and federation does not require hybrid connectivity between the on-premises network and Google Cloud or between Azure and Google Cloud.
Synchronization supports centralized access control in Google Cloud in three ways:
- Provision users automatically from the authoritative source instead of creating them manually, and keep Cloud Identity users as a subset of identity provider users to avoid orphaned accounts.
- Synchronize groups in addition to users so that memberships from Entra ID or Active Directory can control who has access to Google Cloud resources through IAM.
- Use routable primary email addresses that match real mailboxes or aliases so budget alerts, payment notifications, project invitations, and support replies reach billing and support owners.
Single Sign-On with External Identity Providers
Single Sign-On with an external identity provider (opens in a new tab) delegates Google authentication to Active Directory Federation Services, Entra ID, or an identity as a service using the Security Assertion Markup Language protocol. In service provider–initiated SSO, Google Sign-In redirects the user to the external provider, the provider authenticates the user and returns a signed SAML assertion containing the user's email, and Google establishes a session valid across Google services. Some providers also support provider-initiated SSO, where the user authenticates first at the provider and then follows a link to a Google service. Super-admin users are exempt from required SSO and can still sign in with username and password, which preserves administrative access if the provider is unavailable.
A typical workforce sign-in flows from Google to the external provider and back to the protected resource in order:
- Google prompt: The user requests a Google Cloud resource and Google Sign-In prompts for the primary email address.
- Provider redirect: Google redirects the user from
accounts.google.comto the sign-in page of the external provider. - Provider authentication: The user authenticates at the provider, including any second factor required by the provider.
- Return with assertion: The provider returns a SAML assertion to Google, and Google redirects the authenticated user back to the protected resource.
Choosing an Identity Architecture
An identity architecture is chosen by deciding which system will provision identities and which system will authenticate them. Google can serve as both provider and authoritative source, Google can serve as provider with a human resources system as source, or an external system can serve as provider with Active Directory, Entra ID, or an identity as a service as source. Applications that need protocols not offered by Cloud Identity, such as WS-Trust or WS-Federation, can continue to use Active Directory Federation Services (opens in a new tab) directly from Google Cloud, but then Google API calls must use a service account because there is no Google user credential.
| Architecture | Provisioning source | SSO provider | Choose when |
|---|---|---|---|
| Google as provider and authoritative source | Cloud Identity Premium or Google Workspace | There is no on-premises provider to integrate and no HRIS requirement | |
| Google as provider with HRIS source | HRIS provisions users to Cloud Identity | Onboarding and offboarding are driven by an existing HRIS | |
| External IDaaS as provider and source | IDaaS provisions users and groups to Cloud Identity | IDaaS such as Okta or Ping Identity | The organization already uses an IDaaS and wants one SSO experience across Google and other apps |
| Entra ID as provider with Active Directory source | Entra ID provisions users and groups, often connected to on-premises Active Directory | Entra ID, possibly chained to on-premises AD FS | The organization already uses Entra ID integrated with Active Directory and wants no extra on-premises software |
Maintaining Consistent Security and Access Control
Maintaining consistent security means enforcing the same lifecycle, session, and multi-factor rules in Google as in the corporate directory. The external provider should remain the enforcement point for multi-factor authentication, while Google enforces Google 2-step verification and post-SSO verification for super-admin users who bypass the provider. Session lengths must align so policy intent holds: the default Google Sign-In session is 14 days, the Google Cloud console and API session length is separately controllable, the Admin console session is fixed at 1 hour, and the provider session should be shorter than the Google session so expiration forces users to re-enter credentials instead of silently re-authenticating. To avoid bypass, do not restrict SSO by network mask, minimize SAML attributes to only those required by Google Sign-In, and keep the default google.com issuer and audience unless multiple Cloud Identity accounts require domain-specific issuers.
Lifecycle consistency depends on propagating changes from the provider to Cloud Identity without delay. When an employee leaves, suspend and then delete the matching Cloud Identity user after the retention period, and rename suspended accounts to a non-conflicting name such as obsolete-yyyymmdd-alice@example.com if immediate deletion would violate data-retention needs. For super-admin resilience, place super-admins in a dedicated organizational unit with SSO disabled or enforce post-SSO verification if provider-initiated SSO is still allowed. For business-continuity designs, avoid making Google Cloud depend on the same Entra ID or AD FS whose outage the Google deployment is meant to survive.
Exam tip: Configure the identity provider session to be shorter than the Google session so a Google expiration requires fresh credentials; a longer provider session causes silent re-authentication that defeats a shorter Google session.
Key Facts
- Gated ingress requires all inbound API calls to pass through Apigee before reaching backends, with traffic flowing from the remote network over VPN or Interconnect to a Private Service Connect endpoint, then to an internal load balancer and application APIs.
- A Private Service Connect endpoint exposes a producer service to a consumer VPC, while a Private Service Connect interface lets a producer VM reach into a consumer VPC and on-premises sources reachable through that VPC.
- Cloud VPN encrypts traffic by default with IPsec, while Cloud Interconnect requires HA VPN over Cloud Interconnect or MACsec for encryption.
- HA VPN gateways receive two external IP addresses and can provide 99.99% or 99.9% availability, while a gateway with only one active interface provides no availability SLA.
- Identity federation provisions users one-way from the corporate directory into Cloud Identity and delegates authentication to an external provider with SAML, matching the NameID claim to the Google primary email address.
Frequently Asked Questions
What is the difference between a Private Service Connect endpoint and a Private Service Connect interface in Google Cloud?
A Private Service Connect endpoint exposes a service published in a producer Virtual Private Cloud (VPC) to a consumer VPC, while a Private Service Connect interface lets an application virtual machine in the producer VPC reach into the consumer VPC. Endpoint traffic flows from the consumer VPC to the producer service to expose Google APIs or application backends as a private address, while interface traffic flows from the producer virtual machine into the consumer VPC and beyond to retrieve data from sources in that VPC or from on-premises networks reachable through that VPC.
When should I use Cloud VPN instead of Partner Interconnect or Dedicated Interconnect for hybrid connectivity?
Cloud VPN uses IPsec VPN over the public internet and is chosen for lower cost, lower bandwidth needs, experimenting with migration, or occasional low-volume exchange. Partner Interconnect provides private transport through a service provider for larger data transfers with dedicated capacity, normally less than 10 Gbps per connection, without managing colocation hardware, while Dedicated Interconnect provides a private direct connection in a colocation facility for typical transfer rates of 10 Gbps or more when the team can manage routers, cross-connects, and a common point of presence.
How does gated ingress with Apigee as the API platform handle inbound API traffic from on-premises or another cloud?
Gated ingress with Apigee requires all inbound API calls to pass through a managed gateway before reaching a backend for controlled entry, authentication and policy enforcement, rate limiting, and analytics. Traffic flows from on-premises or another cloud over Cloud VPN or Cloud Interconnect to a Private Service Connect endpoint in the application Virtual Private Cloud (VPC) associated with the Apigee VPC, then to an internal load balancer that forwards the request to the application APIs, with firewall rules and traffic filtering providing fine-grained access control.
Sample Question
An enterprise is planning to migrate several core business applications to Google Cloud while maintaining its existing Microsoft Entra ID (formerly Azure Active Directory) as the authoritative identity provider (IdP).
The organization wants to implement automated user provisioning and Single Sign-On (SSO) with Cloud Identity to support centralized access control. The architecture must satisfy the following requirements:
- End users must log in to Google Cloud using their existing corporate identity credentials without credential duplication.
- User mapping between Microsoft Entra ID and Cloud Identity must minimize sign-in confusion and ensure notification emails reach user inboxes.
- The identity design must strictly follow Google Cloud domain verification and naming requirements.
Which identity federation strategy should the cloud architect implement?
How learners score on this domain
Last updated