Intermediate
Prepare and test your skills
Intermediate
Prepare and test your skills
Gemini Cloud Assist for Troubleshooting and Optimization
Operational troubleshooting with Gemini Cloud Assist (opens in a new tab) is the process of analyzing logs, metrics, and diagnostic data to find the root cause of infrastructure failures and apply fixes that keep services highly available. Diagnostic data flows from Google Cloud resources into Gemini Cloud Assist, Gemini Cloud Assist compares current behavior against baseline behavior, and hypotheses flow back to the operator as recommended remediation steps. This loop turns raw signals such as latency spikes, CPU pressure, or failed jobs into specific actions like fixing configuration or rerunning a workload.
Diagnostic Loop to Remediation
Process Flow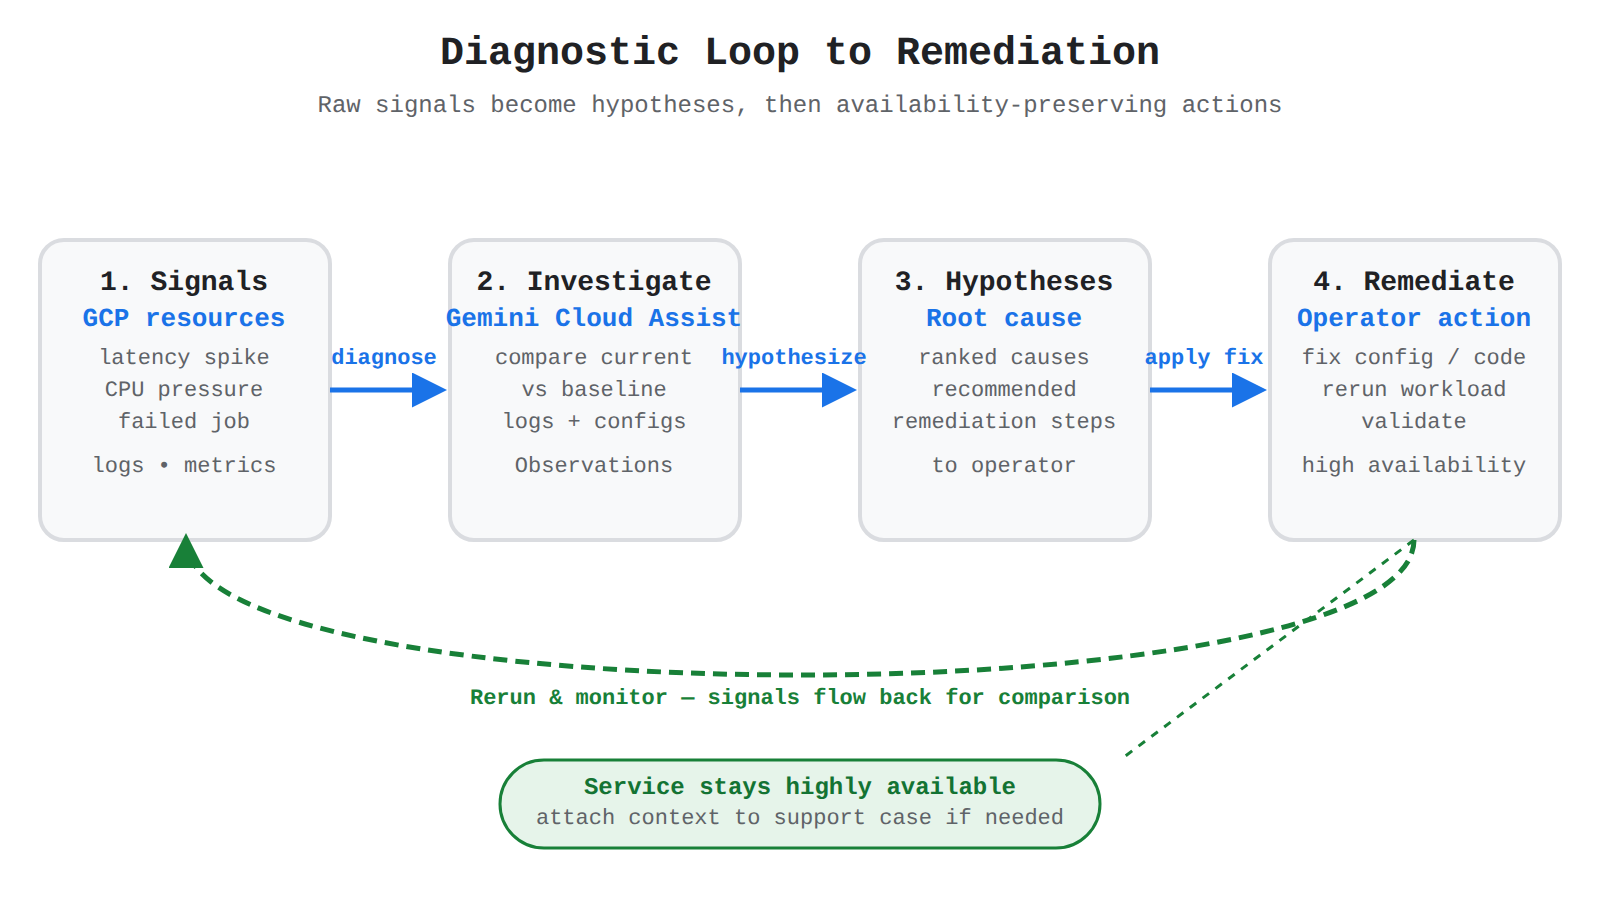
Four-step process flow from signals to investigate to hypotheses to remediate, with diagnostic data flowing forward into Gemini Cloud Assist and fixes flowing back to workloads.
Investigations in the Cloud Assist Panel
Investigations in the Cloud Assist panel are AI-assisted troubleshooting sessions that analyze infrastructure and application issues inside a Google Cloud environment. An investigation depends on both access and context: the user asks for help in the Cloud Assist panel, Gemini Cloud Assist determines whether a deep investigation is useful, and the investigation then runs against logs and performance data for the selected resources and time range. Investigations create persistent analysis that can be reviewed, saved, and attached to a Google Cloud support case to speed up collaboration.
Creating an investigation from chat follows an ordered workflow:
- Ask for help: Ask Gemini Cloud Assist chat to investigate or troubleshoot an issue with Google Cloud resources.
- Offer to investigate: If an investigation would be useful, a Create investigation button appears in the chat.
- Confirm context: Click Create investigation to open the creation panel, where fields are pre-populated from the chat, then edit or add relevant details.
- Run and review: Click Create to open Investigation details while Gemini Cloud Assist runs the analysis.
Exam tip: Chat-based investigations require a Premium Support contract or approved access plus the Investigation Creator IAM role; without both, the Create investigation option will not work.
Bigtable Performance Investigations
Bigtable (opens in a new tab) investigations identify the root cause of database performance problems such as CPU utilization spikes or increased latency. The operator selects an instance, opens System insights, and starts an investigation for a specific cluster and time range, so Gemini Cloud Assist knows exactly which performance window to compare against baseline behavior. When analysis finishes after a few minutes, the Investigation Overview pane separates what happened from what to do next.
Starting a Bigtable investigation follows this order: first open the instance list and open the instance, then click System insights, then click Explore Investigations, then select the cluster and time range, then click Investigate. Gemini Cloud Assist analyzes performance data for the selected period by comparing baseline aggregated data against current behavior across five signal areas:
- Client latencies
- Server latencies
- CPU utilization
- Disk utilization
- Request count
When Gemini Cloud Assist detects a significant change, the investigation names a possible root cause and lists actionable insights in Hypotheses. Findings can include observations such as client misconfiguration details, for example an incorrect channel pool size, while Hypotheses lists AI-recommended actions to address the anomalies. In some situations the analysis completes without a recommendation, which means no significant actionable cause was detected for that time range.
Spark Batch Workload Investigations
Managed Service for Apache Spark (opens in a new tab) investigations analyze failed and slow-running batch workloads to identify root causes and recommend fixes. Managed Service for Apache Spark is the current name for the product formerly known as Dataproc on Compute Engine for cluster deployment and Google Cloud Serverless for Apache Spark for serverless deployment. Before starting, the Gemini Cloud Assist API must be enabled in the project, and the operator can add a natural language description to give the issue context.
Investigations can be started from two console locations. Option 1 starts from the Batches List page, where any batch with a Failed status shows an INVESTIGATE button in the Insights by Gemini column. Option 2 starts from the Batch Details page, where both Succeeded and Failed batches show an INVESTIGATE button in the Insights by Gemini panel inside the Health overview section of the Summary tab. The button text shows the lifecycle state of the analysis: INVESTIGATE means no investigation has run, INVESTIGATING means analysis is in progress, and VIEW INVESTIGATION means results are ready to view.
Once complete, the Investigation details page organizes the full analysis into three sections. Issue contains auto-populated details of the batch workload being investigated. Relevant Observations lists key data points and anomalies that Gemini found during analysis of logs and metrics. Hypotheses is the primary expanded section, where each potential root cause includes an overview such as high shuffle write time and potential task skew, plus a list of recommended fixes.
From Diagnosis to Remediation
Remediation from diagnosis is the step where diagnostic conclusions become availability-preserving action. After reviewing hypotheses and recommended fixes, the operator applies one or more suggested fixes to the job configuration or code and then reruns the job, so the fix flows from the investigation back into the workload. Results can be revisited from the Cloud Assist Investigations page by opening the investigation name, and feedback can be left with thumbs-up or thumbs-down icons.
The two database and batch investigation types differ in what they analyze and where they start:
| Investigation type | What it analyzes | Where it starts |
|---|---|---|
| Bigtable investigation | Cluster performance over a selected time range using latency, CPU, disk, and request-count signals | Instance System insights and Explore Investigations |
| Managed Service for Apache Spark investigation | Failed or slow batch workload using batch logs and metrics plus operator-provided context | Batches List page for failed batches or Batch Details Health overview for succeeded and failed batches |
If further help is needed, the operator can open a Google Cloud support case with the full investigation context attached, which lets support see the same issue details, observations, and hypotheses.
Security posture management with Gemini Cloud Assist (opens in a new tab) is the practice of using AI assistance to find weaknesses, explain risks, and guide fixes across Google Cloud. Gemini Cloud Assist is an AI-powered collaborator built as a multi-agent ecosystem that can reason dynamically, make iterative tool calls, and keep memory across complex tasks. It understands infrastructure, application code, organizational policies, and real-time operational state, which lets it move teams from reactive troubleshooting toward proactive security operations.
How Gemini Cloud Assist Sees Your Security Context
How Gemini Cloud Assist sees your security context is determined by your project ID and organization ID, page context awareness, and memory of the conversation. Page context awareness means the current Google Cloud console page, including the page URL and all visible text, is used as context so responses stay specific to the resource you are viewing. Memory stores session history and key details across multiple turns, so follow-up questions about the same cluster, image, or policy stay connected. Gemini Cloud Assist has the same permissions as the user who asks the question, so it can only discover and explain assets, policies, and configurations that user is already allowed to see.
Finding Artifact Vulnerabilities with Gemini Assistance
Artifact vulnerability review with Gemini Cloud Assist uses Artifact Analysis data to answer questions about repositories, artifact metadata, vulnerabilities, and software bill of materials (SBOMs). The flow starts in the Cloud Assist panel in the Google Cloud console, where a prompt is sent to Gemini Cloud Assist and Gemini Cloud Assist queries scan results for artifacts stored in Artifact Registry. This requires Gemini Cloud Assist setup in the project, billing enabled, and the Artifact Registry and Container Scanning APIs enabled. Once enabled, teams can ask focused security questions such as:
- Top known vulnerabilities affecting artifacts in the project
- Images affected by a specific vulnerability
- Images affected by a specific package
- Build provenance for an image
- SBOMs that list components inside an image
These questions connect scan data to action because Gemini Cloud Assist links a vulnerability to the images and packages that contain it, and links an image to its provenance and SBOM for deeper review.
Detecting Misconfigurations and Security Anomalies
Misconfiguration detection with Gemini Cloud Assist combines conversational chat with Gemini Cloud Assist Investigations for deeper, automated analysis. Chat can explain confusing messages, suggest which metrics to check, and describe best practices for securing a Google Kubernetes Engine (GKE) (opens in a new tab) cluster, with related documentation links. Investigations acts as a user-guided site reliability engineer that ingests logs, metrics, and configurations to explore multiple hypotheses in parallel and trace root causes across multi-tier topologies.
An investigation follows an ordered workflow:
- Initiation: The investigation starts from chat, Logs Explorer, an error, or a specific resource in the console, Cloud Mobile App, command-line interface, or IDE.
- Analysis: Gemini Cloud Assist analyzes logs, configurations, and metrics to detect hidden patterns and surface anomalies.
- Hypotheses: The service produces ranked observations and hypotheses about probable root causes.
- Next steps: The service provides recommended next steps, which can be transferred to a Google Cloud support case with environment summaries and logs as context.
Security specialists use this same workflow to identify potential security-related anomalies or misconfigurations, because the investigation connects signals from different tiers instead of showing one log at a time.
Guiding Remediation and Policy Enforcement
Guided remediation with Gemini Cloud Assist turns findings into role changes, code changes, and support actions. For identity risk, Identity and Access Management (IAM) assistance simplifies tasks by selecting roles, explaining existing policies, or generating policies from natural language or guided flows. For infrastructure and organizational policies, Gemini Cloud Assist can iteratively generate or refine Google Cloud CLI commands, kubectl manifests, and Terraform code through chat in App Design Center and the Cloud Assist panel, and simulate the generated policies directly within chat before they are applied. Because Gemini Cloud Assist output can seem plausible but be factually incorrect, every suggested role, policy, or fix must be validated before use.
Access and Permissions Required for Security Work
Access and permissions required for security work include setup for a project or folder plus IAM roles that let the assistant see topology and security configuration. The Cloud Asset Viewer role lets the agent discover asset topology through Cloud Asset Inventory, which manages resources, policies, and configurations. Job-function roles such as Security Auditor add visibility into folder hierarchy, logs, security configuration, and key resource metadata.
The Gemini Cloud Assist roles themselves control what a person can do with the assistant:
| Role | Can invoke and chat | Can manage artifacts and configuration |
|---|---|---|
| Gemini Cloud Assist Viewer | No, view investigations, reports, and agent configurations only | No |
| Gemini Cloud Assist User | Yes, invoke agents, chat, create artifacts, and share owned artifacts | No |
| Gemini Cloud Assist Editor | Yes, with User permissions | Yes, delete chat topics and artifacts and update specific agent configurations |
| Gemini Cloud Assist Admin | Yes, with Editor permissions | Yes, plus configure policies such as proactive agents and data sharing and share artifacts project-wide |
When findings are missing or incomplete, the cause is often access because Gemini Cloud Assist depends on Cloud Asset Inventory data and on the requester's IAM permissions to see the relevant resources.
Exam tip: Gemini Cloud Assist sees only what the requester can see, so add Cloud Asset Viewer plus the product-specific role, such as Security Auditor for posture review, when results are incomplete.
Gemini Cloud Assist (opens in a new tab) for architectural optimization is an AI assistant that helps review Google Cloud designs for better resource allocation, performance, and cost-efficiency. An architect asks natural-language questions in the chat panel, and Gemini Cloud Assist gathers live data from other Google Cloud APIs to answer with context about the actual environment. If supporting APIs are not enabled, Gemini Cloud Assist still responds, but the answers may be more limited in depth or completeness.
Cost and Usage Optimization Features
Cost and usage optimization features in Gemini Cloud Assist are a set of chat and proactive features that connect spending data to the underlying infrastructure. A question about spend flows from the chat panel to cost data sources, and the answer links products, SKUs, resources, and workloads back to specific optimization actions. This connection lets architects check whether a design uses resources efficiently and where waste or unexpected growth is occurring.
The optimization features cover different layers of an architecture:
- Cost optimization for applications, SKUs, products, resources, and workloads answers precise natural-language questions about cloud spend in the chat panel and extends Cloud Hub Optimization and Cost Explorer.
- Cost optimization in FinOps Hub analyzes costs, trends, waste, and utilization with tailored FinOps views and includes AI-drafted summaries for collaboration.
- Proactive cost anomaly analysis runs once a day when an anomaly is detected in a project, identifies the products, SKUs, resources, infrastructure changes, and user or service account behind a spike, and proposes potential fix strategies.
- Database optimization provides AI-driven insights to configure database instances based on usage patterns for potential savings.
- Flow analyzer analyzes network flows and configurations with natural-language queries in Network Intelligence Center.
- Storage Insights answers natural-language questions about Cloud Storage bucket and object usage, configuration, and insights.
Proactive cost anomaly analysis depends on background agent identity, so it runs under a dedicated service account rather than personal credentials. All autonomous actions are audit-logged under that identity, which separates background optimization work from interactive chat work.
APIs That Enable Resource-Aware Recommendations
APIs that enable resource-aware recommendations are the Cloud Asset API (opens in a new tab), Design Center API, App Optimize API, and App Hub API as required foundations for Gemini Cloud Assist. Gemini Cloud Assist calls these APIs to understand inventory, topology, design options, application scope, and cost-utilization data before it generates guidance. Without some or all of these APIs, recommendation quality can be significantly degraded in some use cases.
| API | Role in architectural optimization |
|---|---|
Cloud Asset API (cloudasset.googleapis.com) | Provides a metadata inventory service to understand the resources and topology of the environment |
Design Center API (designcenter.googleapis.com) | Enables design skills that let Gemini Cloud Assist generate resource configurations |
App Optimize API (appoptimize.googleapis.com) | Provides cost-utilization information about cloud spend to improve cost-efficiency of applications |
App Hub API (apphub.googleapis.com) | Lets Gemini Cloud Assist execute queries scoped to App Hub applications, services, and workloads |
Recommended APIs add performance and efficiency signals on top of the required inventory and cost data. The Cloud Monitoring API (monitoring.googleapis.com) supplies resource metrics for analysis and charts, the Cloud Logging API (logging.googleapis.com) adds Data Access audit logs as an extra source for analysis, the Recommender API (recommender.googleapis.com) provides recommendations for improving resource usage and optimizing costs, and the App Topology API (apptopology.googleapis.com) helps Gemini Cloud Assist understand application and resource topology. Additional APIs support specific review needs, including the Cloud Resource Manager API for investigations, the Service Health API for outage information, and the Storage Insights API for creating a Storage Insights dataset for detailed storage questions.
Exam tip: The App Optimize API provides cost-utilization data for optimization, while the Recommender API provides usage and cost recommendations; enable both when a design review needs spend context plus specific rightsizing actions.
Investigations and Agentic Reasoning for Design Review
Gemini Cloud Assist Investigations for design review is an automated, in-depth analysis mode that complements interactive chat for troubleshooting and validating designs. An investigation starts from an error or a specific resource, often launched directly from workflows like Logs Explorer, and Gemini Cloud Assist pulls together logs, configurations, and metrics. The result is a set of ranked findings and next steps that can be transferred to a Google Cloud support case for faster resolution.
An investigation follows an ordered flow:
- Initiation: The user starts the investigation from an error message or a specific resource.
- Data gathering: Gemini Cloud Assist analyzes logs, configurations, and metrics from enabled APIs.
- Hypothesis ranking: The service produces ranked observations and hypotheses about probable root causes.
- Recommendation: The service provides recommended next steps for remediation.
- Handoff: The user can transfer results to a support case to share context with support.
This flow is powered by agentic reasoning, where Gemini Cloud Assist runs dynamic reasoning loops that iteratively invoke tools such as Cloud APIs and Kubernetes APIs to gather data, evaluate state, and choose the next best action. The user-guided multiturn agent preserves context across turns, so an architect can ask for clarification, redirect focus, or change scope without restarting the review.
Key Facts
- Gemini Cloud Assist investigations compare current logs, metrics, and performance data against baseline behavior to produce ranked hypotheses and recommended remediation steps.
- Bigtable investigations analyze client latencies, server latencies, CPU utilization, disk utilization, and request count for a selected cluster and time range.
- Managed Service for Apache Spark investigations use batch logs, metrics, and operator context, with an INVESTIGATE button that changes to INVESTIGATING during analysis and VIEW INVESTIGATION when results are ready.
- Gemini Cloud Assist has the same permissions as the requesting user and depends on Cloud Asset Inventory, so incomplete findings often indicate missing IAM roles such as Cloud Asset Viewer.
- Resource-aware architectural optimization depends on the Cloud Asset API, Design Center API, App Optimize API, and App Hub API, with the Cloud Monitoring API, Cloud Logging API, and Recommender API adding metrics and cost recommendations.
Frequently Asked Questions
What is the difference between a Bigtable investigation and a Managed Service for Apache Spark investigation in Gemini Cloud Assist?
A Bigtable investigation analyzes cluster performance over a selected time range using client latencies, server latencies, CPU utilization, disk utilization, and request count signals and starts from instance System insights and Explore Investigations, while a Managed Service for Apache Spark investigation analyzes failed or slow batch workloads using batch logs and metrics plus operator-provided context. A Bigtable investigation is started for a specific cluster and time range, while a Spark investigation is started from the Batches List page for failed batches or from the Batch Details Health overview for succeeded and failed batches.
How do I start an investigation from chat in the Gemini Cloud Assist panel?
Ask Gemini Cloud Assist chat to investigate or troubleshoot an issue with Google Cloud resources, and if an investigation would be useful a Create investigation button appears in the chat. Clicking Create investigation opens the creation panel where fields are pre-populated from the chat for editing, and clicking Create opens Investigation details while Gemini Cloud Assist runs the analysis against logs and performance data for the selected resources and time range.
What permissions are required to use chat-based investigations in Gemini Cloud Assist?
Chat-based investigations require a Premium Support contract or approved access plus the Investigation Creator Identity and Access Management (IAM) role. Without both, the Create investigation option will not work.
Which APIs are required for resource-aware architectural optimization recommendations in Gemini Cloud Assist?
Resource-aware recommendations require the Cloud Asset API, the Design Center API, the App Optimize API, and the App Hub API, which provide inventory and topology, design skills, cost-utilization data, and application-scoped queries. Without some or all of these APIs, recommendation quality can be significantly degraded in some use cases.
Sample Question
An enterprise has deployed a multi-tier web application across Compute Engine virtual machines and Google Kubernetes Engine (GKE) clusters. Over several months of production traffic, operations teams have noticed rising infrastructure costs alongside intermittent performance bottlenecks during unexpected traffic spikes. As the lead cloud architect advising the team, you need to evaluate the current architecture against the Google Cloud Well-Architected Framework to optimize resource allocation, improve cost-efficiency, and enhance performance.
Which approach should you recommend to achieve these architectural optimizations using Gemini Cloud Assist?
How learners score on this domain
Last updated