Fundamental
Prepare and test your skills

Fundamental
Prepare and test your skills
Confidential Computing Protects Data in Use
Free sample question with answers and detailed explanation below. The Cloud Digital Leader practice bank has an additional 3,070 practice questions.Try 10 free realistic questions: instant score, no credit card, and no account required.
A healthcare provider is migrating a clinical research workload to Google Cloud. To align with its cloud security model, the organization must uphold the principles of confidentiality and integrity by meeting the following requirements:
- Keep sensitive patient data encrypted while it is actively being processed in memory.
- Perform computation in cryptographic isolation within a multi-tenant cloud environment to prevent unauthorized access or modifications.
- Provide independently verifiable attestations of the system state and the code being executed.
Which Google Cloud capability should the organization implement to meet these requirements?
Explanations
Binary Authorization
Binary Authorization
What Binary Authorization is and does
Binary Authorization is a deploy-time security control that upholds software supply chain integrity for container-based workloads. It ensures that the underlying code and container images for services are verified, signed by trusted authorities, and pass attestation checks before they are allowed to deploy to a production environment.
Why it doesn't meet the requirements
- No encryption of data in use: Binary Authorization does not encrypt sensitive patient data while it is actively being processed in system memory.
- No runtime cryptographic isolation: While it prevents unverified container images from starting, it does not create a hardware-isolated Trusted Execution Environment (TEE) to protect active memory from unauthorized access or modification during computation.
Key characteristics and limitations
- Pre-deployment policy enforcement: Evaluates cryptographic signatures and build attestations against organization policies before workloads are scheduled.
- Supply chain protection: Prevents unreviewed or unauthorized code from being introduced into production environments, either accidentally or maliciously.
- Modeled on internal security controls: Mirrors Google's internal Binary Authorization for Borg (BAB), which verifies production software before it can process customer data.
- Scope limitation: Operates as an admission control gate prior to execution rather than an in-memory encryption mechanism during execution.
This answer would be correct if
The organization needed to enforce software supply chain integrity by requiring that all container images pass automated vulnerability scans and receive cryptographic sign-off before being deployed to Google Kubernetes Engine (GKE) or Cloud Run.
Additional context
In a defense-in-depth security model, Binary Authorization and Confidential Computing complement each other. Binary Authorization upholds integrity at the deployment phase by ensuring only trusted code is launched, whereas Confidential Computing upholds confidentiality and integrity at runtime by isolating and encrypting the workload in memory.
Cloud Key Management Service (Cloud KMS)
Cloud Key Management Service (Cloud KMS)
What Cloud Key Management Service (Cloud KMS) is and does
Cloud Key Management Service (Cloud KMS) is a centralized cloud service that lets organizations create, import, rotate, and manage cryptographic keys. It primarily supports confidentiality and control by enabling customer-managed encryption keys (CMEK) and integrating with Cloud External Key Manager (Cloud EKM) to protect data at rest.
Why it doesn't meet the requirements
- Focuses on data at rest rather than data in use: Cloud KMS manages the cryptographic keys used to encrypt data stored on persistent disks, databases, and storage buckets, but it does not encrypt data while it is decrypted in RAM for active computation.
- No Trusted Execution Environment (TEE): It does not provide hardware-level memory isolation for running workloads or generate attestations of the code being executed in memory.
Key characteristics and limitations
- Centralized key lifecycle control: Allows administrators to define key rotation schedules, control key permissions via Identity and Access Management (IAM), and destroy keys when needed.
- External key separation: Supports Cloud EKM, allowing organizations to store encryption keys outside of Google's infrastructure in a third-party key management system.
- Hardware security module support: Integrates with Cloud HSM to host encryption keys in certified hardware security modules.
- Compatibility with Key Access Justifications: Can require a documented justification and approval before an externally hosted key is used to decrypt data at rest.
This answer would be correct if
The organization wanted to maintain direct control over the cryptographic keys used to encrypt stored patient records at rest, or needed to keep encryption keys physically separated from stored cloud data using an external key manager.
Additional context
By default, Google Cloud automatically encrypts all customer data at rest without any user intervention. Organizations adopt Cloud KMS when compliance mandates require customer control over the key lifecycle for stored data, whereas Confidential Computing is required to protect data while it is actively processed in memory.
Confidential Computing
Confidential Computing
What Confidential Computing is
Confidential Computing is a security technology that encrypts data in use while it is actively being processed in system memory. In a comprehensive cloud security model, Google Cloud protects data across three distinct states: at rest (stored on disk), in transit (moving across networks), and in use (actively being computed). Confidential Computing relies on a hardware-based Trusted Execution Environment (TEE) to provide cryptographic isolation during computation.
TEE Enclave: Encrypted In-Use Processing
System Architecture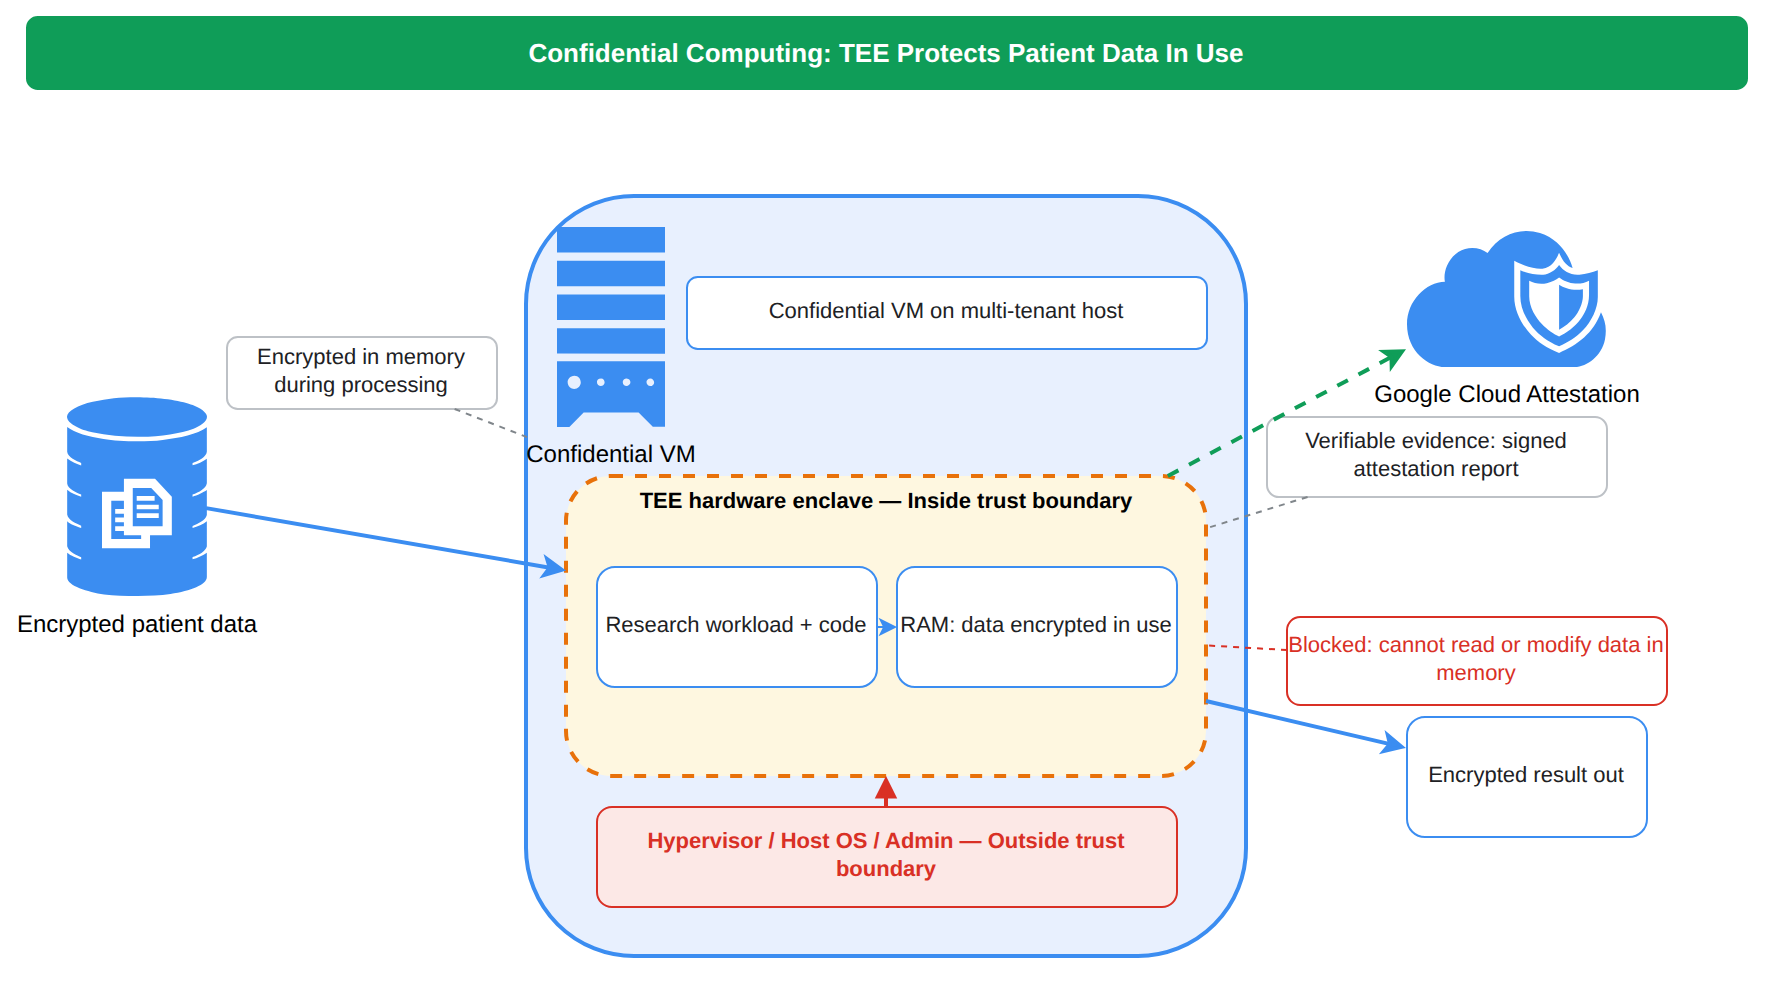
How it meets the requirements
- In-memory encryption: It keeps sensitive patient data encrypted in random-access memory (RAM) during processing, ensuring that data is never exposed in plaintext to the underlying hypervisor, host operating system, or cloud personnel.
- Confidentiality and integrity in a multi-tenant environment: By executing workloads inside a cryptographically isolated enclave, it prevents both unauthorized access (upholding confidentiality) and unauthorized modifications to applications and data while in use (upholding integrity).
- Verifiable attestations: The Trusted Execution Environment (TEE) generates independently verifiable cryptographic attestations that confirm the system state and verify the exact code running inside the enclave.
Key advantages and capabilities
- End-to-end workload protection: Combines with default encryption at rest and Transport Layer Security (TLS) encryption in transit to secure data throughout its entire lifecycle.
- Reduced trust boundary: Limits the number of infrastructure components and administrative roles that can view or alter sensitive workloads.
- Broad service support: Available across Confidential VM, Confidential Google Kubernetes Engine (GKE) Nodes, Confidential Dataflow, Confidential Managed Service for Apache Spark, and Confidential Space.
- Regulatory compliance readiness: Provides verifiable privacy and security assurances for organizations managing strictly regulated healthcare or financial data.
Why this is optimal
While standard encryption at rest and Identity and Access Management (IAM) restrict who can access stored data, and redundancy ensures high availability across regions, only Confidential Computing extends cryptographic protection and integrity verification directly into active system memory during execution.
Access Transparency
Access Transparency
What Access Transparency is and does
Access Transparency is a logging and monitoring service that provides customers with near real-time audit logs whenever Google personnel access customer content. It upholds the security principles of control, visibility, and accountability by recording administrative actions taken during support events or outage recovery.
Why it doesn't meet the requirements
- Detective logging rather than preventive encryption: Access Transparency records administrative access events after or as they happen, rather than encrypting patient data in memory during processing.
- No workload isolation: It does not provide a Trusted Execution Environment (TEE) or cryptographic isolation to prevent unauthorized modifications to applications and data while they are in use.
- No code attestation: It logs human support justifications rather than generating hardware-level cryptographic attestations of system state and running code.
Key characteristics and limitations
- Business justification tracking: Captures the specific reason code—such as a customer-initiated support ticket ID or an outage recovery event—whenever authorized personnel interact with resources.
- Integration with Access Approval: Works alongside Access Approval, which allows customers to explicitly approve or deny access requests from Google support personnel before access is granted.
- Support for compliance: Helps regulated organizations demonstrate auditability and oversight over cloud provider administrative activities.
- Operational scope: Focuses strictly on monitoring provider access rather than performing cryptographic operations on workload memory.
This answer would be correct if
The organization needed to strengthen compliance and accountability by capturing immutable audit logs containing a verified business justification every time a Google administrator accessed their environment to resolve a support ticket.
Additional context
Logging services like Access Transparency and Cloud Audit Logs are vital detective controls in a cloud security model. They provide visibility into who accessed data and why, working alongside preventive controls like Identity and Access Management (IAM) and Confidential Computing.
Try 10 interactive questions like this one, free
Answer them yourself and get your score the moment you finish. No account needed.
Full access includes
- 3,070 practice questions across all 6 exam domains
- Every answer explained: why it is right, and why the others are not
- Scout, an AI tutor that answers your follow-up questions
- Readiness tracking by domain, so you know when to book the exam
Related free sample questions
Keep the momentum going with these hand-picked practice scenarios
FundamentalCloud Digital Leader
Audit Manager Compliance Reports
Describe the importance of control, compliance, confidentiality, integrity, and availability in a cloud security model.
FundamentalCloud Digital Leader
Cloud Billing Budgets vs Resource Quotas
Discuss how Google Cloud supports an organization's financial governance and ability to control their cloud costs.
FundamentalCloud Digital Leader
PaaS Shared Responsibility Model
Discuss the benefits and tradeoffs of using infrastructure as a service (IaaS); platform as a service (PaaS); and software as a service (SaaS).
FundamentalCloud Digital Leader
GKE Managed Kubernetes Orchestration
Define the main cloud compute terms, including: virtual machines (VMs); containerization; containers; microservices; serverless computing; preemptible VMs; Kubernetes, autoscaling, load balancing.
FundamentalCloud Digital Leader
BigQuery and Vertex AI Integration
Explain why and how the cloud is revolutionizing businesses.
FundamentalGenerative AI Leader
Gemini Advanced Custom Gems
Recognizing the functionality, use cases, and business value of the Gemini app and Gemini Advanced (e.g., Gems)
Last updated